A small flaw in a device that is supposed to protect your network can often let an attacker in, which surprises me. That's exactly what happened with the new proof of concept (PoC) that was just released for the Cisco ASA/FTD zero-day vulnerability.
You can imagine that your firewall is the wall that protects your surroundings and keeps them safe at some point. People are less likely to trust perimeter fortifications when attackers use them to get in. This time, the attack is really secret. It first gets past authentication, and then it runs code on a computer that isn't close by.
If your company uses Cisco's Adaptive Security Appliance (ASA) or Firepower Threat Defense (FTD) with WebVPN (clientless VPN) turned on, you could already be at risk. The Cisco ASA FTD zero-day vulnerability PoC makes this threat very real. Let me tell you how it works, why it's important, and what you need to do.
September 2026 Update: Why This Cisco ASA/FTD Threat Still Matters
The original zero-day story did not end with the September 2025 patches. Cisco's latest verified guidance shows that the same broader ArcaneDoor campaign evolved into a persistence problem that security teams still need to account for in 2026.
Cisco says evidence strongly indicates that attackers used CVE-2025-20333 and CVE-2025-20362 to compromise vulnerable Cisco Secure ASA and FTD devices before customers upgraded to the fixed September 2025 releases. In April 2026, Cisco and CISA disclosed a newly identified persistence mechanism in the Firepower eXtensible Operating System (FXOS) on certain hardware platforms. That mechanism could remain present even after a device was upgraded to the older fixed releases.
This changes the defensive question. Teams should not only ask, "Is the vulnerability patched?" They also need to ask, "Could this device have been compromised before it was patched?" That distinction is central to modern network security, because an edge device can remain a trusted gateway even after an attacker has gained persistent access.
For the latest vendor status, Cisco maintains its Continued Attacks Against Cisco Firewalls response page. CISA also maintains Emergency Directive ED 25-03 for organizations that need to identify, investigate, and remediate potentially compromised Cisco devices.
Quick Answer: Is the Cisco ASA/FTD Exploit Still Relevant in 2026?
Yes, but the risk now has two separate parts:
Unpatched vulnerability risk: Devices still running vulnerable ASA or FTD software can remain exposed to the CVE-2025-20333 and CVE-2025-20362 exploit chain.
Post-compromise persistence risk: Certain hardware platforms that were compromised before patching may require more than a normal software update because the later-discovered persistence mechanism can survive the older patching process.
That is why organizations should combine patch management with vulnerability management, asset inventory, threat hunting, and incident-response validation instead of treating the issue as a one-time firmware update.
CVE-2025-20333, CVE-2025-20362, and CVE-2025-20363 at a Glance
| CVE | Main issue | Authentication | Main impact | Confirmed role in the ArcaneDoor chain |
|---|---|---|---|---|
| CVE-2025-20333 | Buffer overflow in the VPN web server | Valid VPN credentials normally required | Remote code execution as root | Yes, when chained with CVE-2025-20362 |
| CVE-2025-20362 | Missing authorization / restricted URL access | No authentication required | Access to protected VPN web endpoints | Yes |
| CVE-2025-20363 | Separate web-services memory corruption issue | Depends on Cisco platform | Remote code execution as root | Cisco's campaign evidence specifically identifies CVE-2025-20333 and CVE-2025-20362 |
The most important distinction is that CVE-2025-20333 is the code-execution vulnerability, while CVE-2025-20362 removes the authentication barrier. Chaining them can turn an authenticated RCE path into an unauthenticated compromise path. CVE-2025-20363 is serious, but it should not be described as the same confirmed two-vulnerability exploit chain unless new vendor evidence says otherwise.
How to Tell Whether a Cisco ASA or FTD Device Is Exposed
The exploit chain does not apply equally to every Cisco firewall. Exposure depends on the software release and whether a vulnerable remote-access VPN feature is enabled.
For Cisco Secure ASA, Cisco lists potentially vulnerable configurations that include:
AnyConnect IKEv2 Remote Access with client services
Mobile User Security (MUS)
SSL VPN / WebVPN
For Cisco Secure FTD, potentially vulnerable configurations include:
AnyConnect IKEv2 Remote Access with client services
AnyConnect SSL VPN
Administrators should verify the running configuration and exact software release rather than assuming that the product name alone proves exposure. Cisco also states that Secure Firewall Management Center (FMC) is not affected by CVE-2025-20362.
The safest inventory process is to identify every internet-facing ASA/FTD appliance, record its software train, confirm whether remote-access VPN services are enabled, and compare the device against Cisco's current fixed-release guidance.
Why End-of-Life ASA Hardware Needs Special Attention
Some ASA 5500-X models involved in this broader threat story are already out of support. Cisco's CVE-2025-20362 advisory lists the ASA 5512-X and 5515-X as having reached last support in August 2022, the 5525-X, 5545-X, and 5555-X in September 2025, and the 5585-X in May 2023.
Cisco published final emergency software releases for certain older 9.12 and 9.14 trains, but an organization should not interpret that as a long-term lifecycle extension. Unsupported perimeter hardware should be migrated to a supported platform because future vulnerabilities may not receive the same remediation path.
Timeline: How the Cisco ASA/FTD Threat Evolved
| Date | Development |
|---|---|
| May 2025 | Cisco became involved in investigations of attacks targeting ASA 5500-X devices with VPN web services enabled. |
| September 25, 2025 | Cisco disclosed CVE-2025-20333, CVE-2025-20362, and CVE-2025-20363; CISA issued ED 25-03. |
| October 2025 | Public technical analysis showed how CVE-2025-20362 could be chained with CVE-2025-20333 and demonstrated a crash-triggering PoC. |
| November 5, 2025 | Cisco reported a new attack variant that could force affected, unpatched ASA/FTD devices to reload and create a denial-of-service condition. |
| April 23, 2026 | CISA and NCSC disclosed FIRESTARTER and updated the Cisco emergency response; Cisco published the FXOS persistence advisory. |
| May 19, 2026 | Cisco updated the persistence advisory and its current fixed-release guidance. |
This timeline explains why a page written only around the original September 2025 zero-day disclosure can become stale even if the CVE numbers have not changed.
What is the zero-day security hole in the Cisco ASA/FTD?
In September 2025, Cisco handed out a security warning to let consumers know about a group of big security weaknesses in its ASA and FTD devices. In the actual world, two of these, CVE-2025-20333 and CVE-2025-20362, have been used.
• CVE-2025-20362 is an issue that lets you get past authentication. It lets users who don't have the right credentials go to web endpoints that should be safe.
• CVE-2025-20333 is a problem with WebVPN's file upload handler that lets too much data into a buffer. In some cases, it lets code run on a remote computer.
They work together to create a fatal exploit chain: they get around the login first, and then they take control via overflowing RAM. Cisco also mentioned a third flaw, CVE-2025-20363, that people would probably use soon. These flaws are especially serious because they affect the WebVPN interface for VPNs. People often turn this option on so that people who are not on the same network can log in over HTTPS. This makes it available on the internet. Because of CVE-2025-20362, attackers may not even need any credentials. The PoC for the Cisco ASA FTD zero-day vulnerability is significantly more deadly now.
Getting around authentication and buffer overflow in the two-stage exploit chain
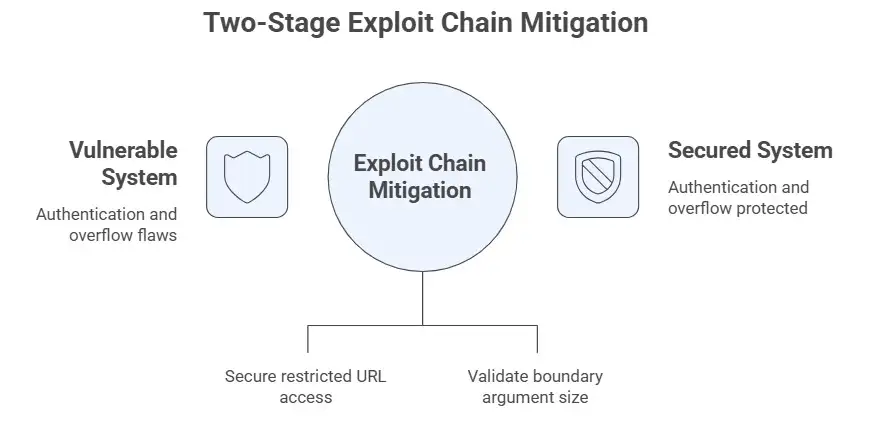
The exploit chain is more than just a problem. This is a planned set of flaws, and each one makes the next step possible.
Step 1: Use path traversal to get around authentication.
The entry point is CVE-2025-20362. Attackers can employ path traversal or path normalization weaknesses to go to restricted URLs without logging in since there is a hole in the authorization process.
For instance, a keycard system that doesn't check if you can get to the second floor anymore. You didn't swipe your card, but the door opens. Attackers can utilize the bypass to call endpoints that only logged-in users can access.
If they are successful, the system may send back a message like "CSRF token mismatch" to let them know that the request went through.
Step Two: Start a buffer overflow to get RCE.
The attacker can now reach CVE-2025-20333 because the protected endpoints are no longer closed. This issue is in the Lua script that handles file uploads. It has to do with whether or not it checks a "boundary" argument. The code expects that a size check will happen; however, it doesn't work well in versions that can be hacked.
The attacker provides a boundary string that is bigger than 8,192 bytes, which is the size of the buffer that is thought to be secure. This makes the buffer overflow. This can hurt memory and let anyone run code on the ASA/FTD device with root access. In real life, attackers link stage one to open the door and then stage two to gain control of the gadget. Rapid7's in-depth research supports this exploit chain.
How the PoC and Exploit Work in Real Life
Cisco and researchers first said there was no public proof-of-concept (PoC), but that changed when researchers made vulnerability code public.
The PoC uses the bypass to reach the file upload endpoint. Then it sends a multipart HTTP request with a boundary that is too big, which breaks the RAM. Some versions of the exploit make this easy by connecting the two parts.
The attack worked in the lab on select versions of ASA/FTD firmware, notably on devices that run ASA software 9.12, 9.14, and other versions that weren't fixed.
One difficult factor is that memory layouts are different in real deployments, security measures like ASLR can make it tougher to exploit, and device settings are different. But attackers who are good at tinkering with memory can change it.
In some cases that have been reported, opponents used this exploit chain to put a bootkit (RayInitiator) and a loader (LINE VIPER) on the machine and make sure they stayed there.
An attacker might scan public IPs, discover a WebVPN front end, and then send the request to get around it. If they are successful, they immediately start the buffer overflow process and take control, usually without anyone noticing. That's how the proof of concept for the Cisco ASA FTD zero-day flaw turns into a weapon.
What the Public PoC Actually Demonstrates
There is an important difference between a public proof of concept and a fully weaponized remote-code-execution exploit.
Rapid7's published research demonstrates how CVE-2025-20362 can be used to reach the vulnerable file-handling path associated with CVE-2025-20333 and how an oversized request can trigger memory corruption. Its public PoC is designed to overflow the affected buffer and crash or reload the vulnerable lina process. Rapid7 explicitly states that the PoC does not go on to achieve arbitrary code execution.
Cisco's advisory still rates CVE-2025-20333 as a critical vulnerability capable of code execution as root under the required conditions. The practical lesson is that defenders should not wait for a reliable public full-RCE exploit before acting. Real-world exploitation was already confirmed by Cisco, and active exploitation should carry more weight than whether a public script performs every stage of the attack.
For security teams, this is also a reminder to use PoCs carefully. Testing a crash-triggering exploit against a production firewall can create an outage. Authorized validation should follow controlled infrastructure penetration testing procedures and vendor-safe checks rather than uncontrolled production exploitation.
What happens in the actual world: Who is in danger, and what is being attacked?
This isn't just a guess. There are still thousands of Cisco ASA/FTD devices that are connected to the internet that need to be fixed. TechRadar said that the new problems could affect about 50,000 firewall devices all across the world.
The effects are quite big:
• Full device compromise: Once attackers get root access to a device, they can change settings, steal network traffic, create backdoor accounts, turn off logging, and even rewrite firmware or ROM.
• Stealth and persistence: Malware like RayInitiator can change the boot sequence or firmware on your computer so that it stays there even after you restart or upgrade it.
• Network pivoting: The hacked ASA/FTD is at the edge of the network. If you have control there, you can see traffic, get in from the side, and get in even further.
• Espionage and targeted attacks: Many of the attacks that have occurred are espionage attempts that focus on networks that are important to the government, defense, or critical infrastructure.
If you have ASA 5500-X series or Firepower devices that expose WebVPN as part of your infrastructure, your risk is not small, especially if you haven't updated the firmware or turned off services that you don't use.
The Shadow That Attacks is where it comes from.
According to public sources, UAT4356, also known as Storm-1849, is the group that is using these zero-day flaws.
People think that this group is a well-funded threat actor that may have connections to the government. Previously, they ran the ArcaneDoor campaign, which used old zero-day flaws to attack Cisco edge devices.
They use stealthy implants, switch off logs, intercept management commands, cause forced crashes to cover their tracks, and deeply embed themselves in firmware to spy.
It's interesting that the actors seem to be especially interested in gadgets that are no longer supported or are soon to die. It could be because these devices don't have as good of security.
This campaign reminds us that edge devices are more than just walls that don't do anything. A skilled enemy can use them as weapons.
The 2026 Persistence Shift: FIRESTARTER and FXOS-Level Access
The biggest development after the original disclosures came on April 23, 2026. CISA and the U.K. NCSC disclosed FIRESTARTER, a persistent backdoor associated with the same broader campaign targeting Cisco firewall infrastructure. Cisco's follow-up investigation tied the new persistence mechanism to FXOS, the base operating system used by affected Firepower and Secure Firewall hardware.
This matters because the persistence mechanism can survive upgrading to the fixed software releases that Cisco published in September 2025. In other words, patching can close the original vulnerabilities, but it does not automatically prove that a device compromised before the patch is clean.
Cisco's current persistence advisory says the initial compromise observed in this activity began with exploitation of CVE-2025-20333 and CVE-2025-20362 before customers upgraded. Cisco PSIRT also says it is aware of active exploitation of the persistence issue.
This is exactly where cyber threat intelligence becomes useful. The vulnerability tells defenders what can be exploited. Campaign intelligence tells them how a real adversary is using it, how the attacker maintains access, and which evidence should trigger a full incident response.
RayInitiator, LINE VIPER, and FIRESTARTER Are Not the Same Thing
These names describe different components or stages that appeared across the broader Cisco targeting activity.
RayInitiator was documented as a bootkit used against certain Cisco ASA 5500-X devices.
LINE VIPER is a user-mode capability associated with the campaign and post-compromise activity.
FIRESTARTER is the later-documented persistent backdoor connected to affected Firepower and Secure Firewall platforms and the FXOS-level persistence mechanism disclosed in 2026.
Keeping these names separate matters because the affected platforms, persistence behavior, and recovery requirements are not identical.
Which Cisco Platforms Are Affected by the 2026 Persistence Issue?
Cisco's May 19, 2026 advisory lists the following hardware platforms as affected by the newly disclosed persistence issue, regardless of device configuration:
Firepower 1000 Series
Firepower 2100 Series
Firepower 4100 Series
Firepower 9300 Series
Secure Firewall 1200 Series
Secure Firewall 3100 Series
Secure Firewall 4200 Series
Cisco lists the following as not affected by this specific 2026 persistence issue:
ASA 5500-X Series
Secure Firewall 200 Series
Secure Firewall 6100 Series
Secure Firewall ASA Virtual
Secure Firewall ISA3000
Secure Firewall Threat Defense Virtual
That does not mean every product in the second list was safe from the original 2025 vulnerabilities or campaign. ASA 5500-X devices, for example, were central to the earlier ArcaneDoor activity. The distinction is specifically about the newly disclosed FXOS persistence mechanism.
Cisco's answer: updates, alerts, and repairs
Cisco got back to us right away. On September 25, 2025, the company sent out security advisories and software updates to fix CVE-2025-20333, CVE-2025-20362, and CVE-2025-20363.
Cisco said that businesses should immediately upgrade any ASA, ASAv, or FTD devices that are at risk.
Cisco also made it easier for organizations to check for past compromises by giving them tips on how to discover them, look for hazards, and evaluate core dumps.
Cisco also makes it clear that you can't cure both problems at once; you need the patch.
Cisco is also keeping an eye out for "continued attacks" and has sent out updates to let admins know how attackers are acting, such as by switching off logs or intercepting CLI.
But you have to utilize patches for them to work. That leads to detection, forensics, and best practices that will help keep your devices safe.
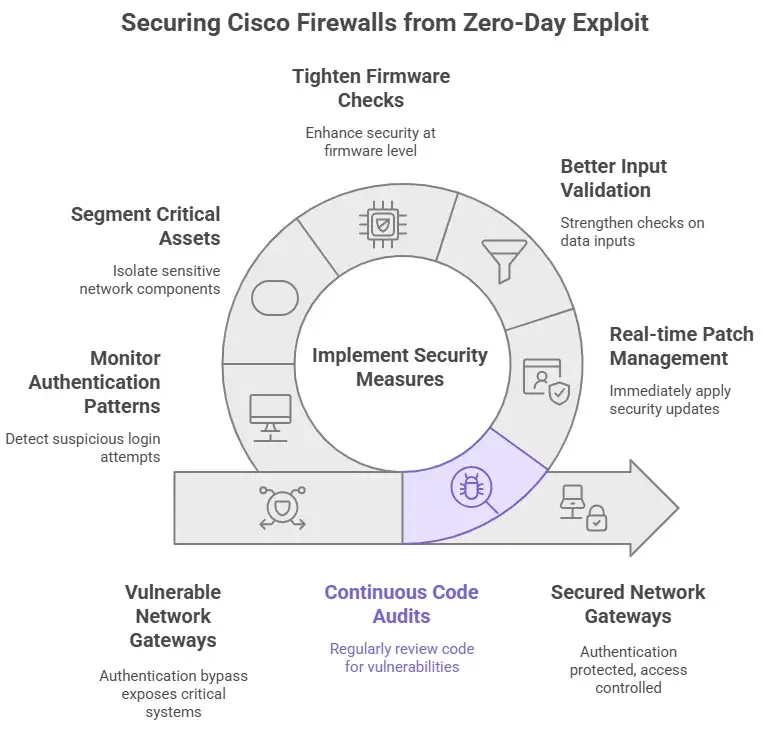
How to Strike a Balance Between Detection and Forensics
This kind of exploit is hard to find since good hackers like to stay hidden. Defenders can still hunt for clues and use forensic methods.
Analysis of core dumps
Cisco and CISA made it possible to get core dumps from ASA/FTD devices, look at them, and figure out what they mean. Even if logs were deleted, these core dumps can still provide memory traces of the intrusion.
Even if forced reboots are used to delete evidence, researchers may still be able to find traces in flash memory or firmware sectors.
Strange behavior
Check for settings that change without warning, services that start up without warning, strange processes, or new user accounts. You should also search for syslog entries that are blocked, CLI commands that are stopped, and system crashes that are forced.
Another positive clue is when WebVPN endpoints get a lot of HTTP requests with strange lengthy strings or boundary parameters. CVE-2025-20362 is about path traversal; therefore, a lot of broken paths could be a sign.
In comparison to the baseline,
Check the current firmware, configuration, file signatures, and modules against known clean baselines. If something changed, someone could have messed with it.
Forensics on a network
Network records may show strange traffic patterns if hackers steal data or send messages back through WebVPN or ICMP channels. This is especially true when connections are made to unusual IPs or command-and-control sites.
The ASA/FTD device is the gateway; therefore, keeping track of its own traffic and internal logs can help show lateral movement.
Using host forensics, configuration auditing, and network monitoring together can help defenders find a stealthy breach more readily.
New 2026 Indicator: How to Check for the lina_cs Process
Cisco's 2026 persistence advisory identifies a malicious process named lina_cs as an indicator that can appear on compromised devices. Administrators can check for it with the vendor-documented command:
show kernel process | include lina_csIf the command returns output, Cisco says the device should be treated as potentially compromised and investigated. However, there are two important limitations.
First, Cisco warns that the implant's process name could change, so the absence of lina_cs does not prove that a device is clean. Second, Cisco has observed a legitimate lina_cs process becoming stuck in some ASA environments, which can create a false positive. Cisco therefore documents an additional verification workflow using an ASDM image signature check before deciding whether the process is malicious.
Defenders should combine this IOC with core-dump analysis, configuration review, external logs, suspicious outbound connections, unexplained reloads, and the wider evidence described in Cisco's detection guidance. A strong incident response and recovery process should treat the firewall as part of the evidence, not as a trusted observer of its own compromise.
Cisco also lists Snort rule 65340 for CVE-2025-20333 and rule 46897 for CVE-2025-20362 in its event-response guidance. These signatures can support detection, but no single IOC or rule should be treated as conclusive.
The safest ways to use ASA/FTD devices
Right away, fix it. That's clear, but it can take a long time. The Cisco ASA FTD zero-day issue PoC only works if the firmware is not upgraded. Cisco recommends you should update your devices to the fixed versions.
If you don't need WebVPN (clientless SSL VPN), turn it off. There are fewer ways for intruders to get in because the surface is less exposed.
Limit who can access management interfaces. Allow access to ASA/FTD admin panels only from inside the network, and use network segmentation. Don't allow the general internet to see these kinds of links.
People who need to use the VPN should use multi-factor authentication (MFA) and certificate-based access. Even if one of the holes in this example lets attackers get past security, layered defenses nonetheless help keep them from moving around and limit their reach.
Make sure your logging is strong, but additionally check logs from outside the device (for example, stream logs off the device) so that you still have copies even if logging is turned off on the device itself. Set up notifications to go off right away for things that seem strange.
Make backups of your settings often, but don't let them be changed or saved online. You should go back to a backup that you know is clean and start over if someone compromises your device. You should change all of your keys, passwords, and certificates after you get them back. The attacker may have taken them.
Don't trust anything by default; only give people the access they need. Always keep an eye on everything. If ASA/FTD is hacked, segmentation can make it tougher for the hacker to move about.
Run scans using CVE detectors, look for the Cisco ASA FTD zero-day vulnerability PoC on your own devices, and remember that security is something you should do all the time, not just once.
Patching Alone Is Not Enough If the Device Was Already Compromised
For a device that is vulnerable but has no evidence of compromise, the priority is still to move to a Cisco-fixed software release and reduce unnecessary exposure. Cisco states that there are no workarounds that replace the security updates for CVE-2025-20333 and CVE-2025-20362.
For a device that is confirmed or strongly suspected to be compromised, the recovery standard is higher. Cisco recommends reimaging the device and upgrading it to a current fixed release. Cisco also advises treating configuration elements as untrusted, especially local passwords, certificates, and cryptographic keys. Those credentials and trust materials should be reconfigured, replaced, or regenerated during recovery.
A normal reload, reboot, or shutdown command is not sufficient to clear the newly disclosed persistent implant. Cisco documents a physical cold restart as an alternative temporary mitigation because removing power can clear the implant, but Cisco does not recommend this as the primary recovery method due to the risk of database or disk corruption. Reimaging remains the preferred response.
This is a classic case for a Zero Trust security approach: once an internet-facing security appliance is suspected of compromise, defenders should stop assuming that its configuration, logs, credentials, or trust state are reliable.
Original 2025 Exploit-Chain Patch Baselines
For organizations investigating historical exposure, Cisco's event-response guidance lists combined first-fixed releases for the original CVE-2025-20333/CVE-2025-20362/CVE-2025-20363 set. Examples include ASA 9.16.4.85, 9.18.4.67, 9.20.4.10, 9.22.2.14, and 9.23.1.19, plus the final ASA 9.12.4.72 and 9.14.4.28 releases for supported legacy use cases. For FTD, combined first-fixed baselines include 7.0.8.1, 7.2.10.2, 7.4.2.4, 7.6.2.1, and 7.7.10.1; some intermediate software trains require migration to a supported fixed train.
These historical versions answer the question, "Which release closed the original exploit chain?" They should not be confused with the newer 2026 fixed releases for the FXOS persistence issue. An affected hardware platform that may have been compromised before patching should follow the newer reimage-and-upgrade guidance.
Current 2026 Fixed-Release Baseline for the Persistence Issue
Cisco's latest persistence advisory version I verified was updated on May 19, 2026. It lists these first fixed release baselines for affected Cisco Secure ASA software trains:
| ASA train | First fixed release listed by Cisco |
|---|---|
| 9.16 | 9.16.4.92 |
| 9.18 | 9.18.4.135 |
| 9.20 | 9.20.4.30 |
| 9.22 | 9.22.3.5 |
| 9.23 | 9.23.1.32 |
| 9.24 | 9.24.1.11 |
For Secure FTD, Cisco lists updated fixed releases or release-plus-hotfix combinations for the 7.0, 7.2, 7.4, 7.6, 7.7, and 10.0 trains. Because Cisco can revise fixed-release guidance, administrators should verify the exact target build and required hotfix in the current advisory before deployment instead of relying only on a static article.
A Practical Recovery Decision Tree
If the device is unpatched but shows no compromise evidence:
Confirm the exact ASA/FTD release and exposed VPN services.
Use Cisco's current advisory or Software Checker to identify the correct fixed release.
Patch urgently.
Disable unnecessary WebVPN/SSL VPN exposure.
Review external logs and historical telemetry for pre-patch exploitation.
If the device may have been compromised:
Isolate the affected appliance where operationally possible.
Preserve core dumps, logs, configuration evidence, and surrounding network telemetry.
Begin a formal incident investigation.
Reimage the device using Cisco's documented procedure.
Upgrade to the current fixed release.
Rebuild only from trusted configuration material.
Rotate local passwords and regenerate certificates and keys.
Hunt for lateral movement or persistence elsewhere in the environment.
Organizations that continuously prioritize internet-facing vulnerabilities through risk-based vulnerability management are in a better position to shorten the exposure window before an edge-device flaw becomes an incident.
What Comes Next: The Future of Security for Edge Devices
This event illustrates that firewalls, VPN gateways, and edge devices are very good targets. They are the times when trust breaks out. When we defend them, we frequently think they can't be hurt, but their enemies know otherwise.
There may not be any zero days in the WebVPN, SSL modules, SNMP, or APIs of firewall appliances in the future. Manufacturers of devices need to include more security features for memory, code, runtime, and secure boot in their products.
Network operators should be ready for the worst on the defense side and make sure that a breach of a gateway doesn't mean the end of the world. Microsegmentation and zero trust architectures can stop hackers from getting too far into the network.
Hackers will also change PoCs as soon as they are made public. Teams in charge of security need to work rapidly. Now, you need automation, patch orchestration, and proactive scanning.
Last but not least, government agencies, contractors, and security groups need to work together more quickly. Alerts, shared telemetry, and cooperative defense (sharing threat intelligence) all help stop attacks before they get worse.
People will probably use the Cisco ASA FTD zero-day vulnerability proof of concept incident as an example of how to get ready for both attacks and defenses.
Updated FAQ for Cisco ASA/FTD Defenders in 2026
Is CVE-2025-20333 still a zero-day?
It was a zero-day when Cisco disclosed it in September 2025 because exploitation had already been observed. It is no longer an unpatched zero-day today because Cisco has released fixes. The current risk comes from devices that remain vulnerable and from previously compromised systems that may require deeper remediation.
Does a public PoC provide full unauthenticated root RCE?
Not necessarily. The widely cited Rapid7 public PoC demonstrates the authentication-bypass-plus-buffer-overflow chain and can crash the vulnerable lina process, but Rapid7 says its PoC does not continue to arbitrary code execution. Cisco's vulnerability assessment and real-world incident evidence are the reasons organizations should treat the issue as critical.
Does installing the September 2025 patch remove FIRESTARTER?
Not if the device was already compromised with the later-disclosed persistence mechanism. Cisco says that persistence can survive upgrading to the September 2025 fixed releases on affected hardware. Suspected or confirmed compromised systems should follow Cisco's reimage-and-upgrade guidance.
Can a normal reboot remove the persistent implant?
Cisco says the standard shutdown, reboot, and reload commands do not clear the persistent implant described in its 2026 advisory. A physical cold restart can remove the active implant as an alternative mitigation, but Cisco warns about corruption risk and recommends reimaging instead.
Is an ASA 5500-X affected by the new FXOS persistence issue?
Cisco lists ASA 5500-X as not affected by the specific persistence issue disclosed in April 2026. However, ASA 5500-X systems were targeted in the earlier ArcaneDoor campaign, so administrators should not use that distinction to ignore the original 2025 compromise risk.
Was CVE-2025-20363 part of the confirmed two-stage exploit chain?
Cisco's current event-response material says the collected evidence strongly indicates that CVE-2025-20333 and CVE-2025-20362 were used in the campaign. CVE-2025-20363 is a separate critical Cisco web-services RCE vulnerability and should be patched, but it should not be presented as the same confirmed two-stage chain without additional evidence.
Is disabling WebVPN enough?
No. Disabling unnecessary WebVPN or SSL VPN exposure reduces attack surface, but Cisco says there are no workarounds that replace the required software fixes for the affected vulnerabilities. Devices that were previously compromised may also require reimaging.
What should organizations monitor after remediation?
Keep monitoring firewall-originated outbound traffic, configuration changes, authentication activity, unexpected reloads, core dumps, external syslog data, and unusual management-plane behavior. Combine that telemetry with cyber threat intelligence so detection rules evolve as the campaign changes.
Summary and Key Points
Finding and actively using the Cisco ASA FTD zero-day vulnerability PoC is one of the most audacious assaults in a long time. It's not straightforward to link a bypass to a buffer overflow such that someone can get remote root access to firewall devices.
But the lessons are clear: you have to move quickly. A lot of patching. Make your settings more secure. Never think that something is impossible. And always be on the lookout for strange behavior.
Edge devices like ASA/FTD are no longer just walls that keep people out. They become tools for attackers. Get ready.
By being vigilant, acting quickly, and having a strong defense, we can limit the damage and stay one step ahead.
Cisco's official security advisory on ASA/FTD WebVPN vulnerabilities says, "The vulnerabilities, CVE-2025-20362 and CVE-20333, make up an exploit chain that lets an attacker run code on a vulnerable device without having to log in."
The Box of Hoplon Insight
• Check all of the Cisco ASA/FTD devices near you right away.
• Don't wait to install approved patches; they should be at the top of your list of things to accomplish.
• Turn off WebVPN if you don't need it.
• Limit the number of persons from outside who can access the interfaces for managing devices.
• Send logs to a server and set up alerts for WebVPN queries that don't appear right.
• Use the core dump and forensic methods that Cisco and CISA give you to detect risks.
• Change all of the passwords and keys on hacked devices to set them up again from scratch.
• Use zero trust and microsegmentation to keep a breach from doing too much damage.
Hoplon Infosec’s Endpoint Security protects ASA/FTD devices and network endpoints, offering real-time threat detection, monitoring, and rapid response to keep your systems safe.
In 2026, it's a scary fact that firewalls, which we rely on to protect our networks, are becoming the main targets for high-level digital sabotage. The release of a sophisticated Proof of Concept (PoC) for the Cisco ASA/FTD zero-day vulnerability has fundamentally changed how we think about edge security.
Your firewall is like the outside wall of a castle. We thought for years that these walls were impossible to break through. But attackers have figured out how to not only climb the wall, but also get through the front gate by fooling the lock. This attack is especially dangerous because it combines an authentication bypass with remote code execution (RCE), making the protector a backdoor.
If your company uses Cisco's Adaptive Security Appliance (ASA) or Firepower Threat Defense (FTD) with WebVPN (clientless VPN) turned on, you are a target. Let's look at the technical facts about this threat and what needs to be done by 2026.
In late 2025, a serious bug was found that let hackers connect two different vulnerabilities into one deadly exploit chain. By the beginning of 2026, this has turned into a very automated process used by people who work for the government.
Phase 1: The Entry That Can't Be Seen (CVE-2025-20362)
The trip starts with a way to get around authentication. An attacker can get to restricted web endpoints that should require a login by using path traversal techniques. It's like a keycard system that doesn't check who is allowed to enter the most private rooms in the building.
No access to the internal network is needed to start the attack because it happens at the WebVPN interface, which is usually open to the public internet.
Phase 2: Full Control through Buffer Overflow (CVE-2025-20333)
Once the attacker gets around the login, they look for a bug in the Lua script that handles file uploads. They cause a buffer overflow by sending a "boundary" argument that is more than 8,192 bytes long. This messes up the device's memory, giving the attacker root access to run any code they want.
The 2026 Update: The "RayInitiator" Threat and Persistence
As of February 2026, the threat has grown beyond just getting in. Researchers in security have found a new type of "Impairment Malware" that is made just for Cisco ASA/FTD devices.
Firmware Persistence: Hackers are now using bootkits like RayInitiator. These are hidden in the device's low-level firmware (ROMMON), so even a factory reset or a normal software update might not get rid of the infection.
The UAT4356 (Storm-1849) Campaign: People have seen this well-funded group use these weaknesses to attack government and defense networks. They don't want to steal right away; they want to spy on you for a long time. They stop management commands and "silence" logs so that administrators think the system is working fine while they steal data.
Forced Crashes: If an administrator tries to run a forensic tool, the malware can cause the system to crash on purpose to erase any evidence in the volatile RAM, making it very hard to look into the breach.
Strategies for Finding and Forensics in 2026
Standard logging isn't always enough to stop these attacks. To find a breach in 2026, you need to look for "subtle deviations":
CISA and Cisco now suggest looking at core dumps as part of core dump analysis. Even if an attacker deletes logs, memory traces of the buffer overflow are often still in these dump files.
WebVPN Request Spikes: Check for a lot of HTTP requests that have long strings or complicated path traversals, like ../ sequences.
Outbound Anomalies: If your ASA/FTD device starts making its own outbound connections to unknown IP addresses, especially through ICMP or non-standard ports, this is a sign that it is "phone home."
CLI Interception: If the command-line interface is slow or some commands (like show tech-support) give errors, the device may have been hacked and is now hiding the hacker.
Action Plan: Best Ways to Do Things in 2026
If you are in charge of Cisco edge infrastructure, you must do the following:
Immediate Patching: Make sure you are using the Cisco-provided firmware versions that have been validated for 2026. These have fixes for the exploit chain and better memory protection.
Turn off WebVPN: Turn off clientless SSL VPN right away if your company doesn't need it. The best way to protect yourself is to make the attack surface smaller.
Management Plane Isolation: Don't let the public internet see the ASA/FTD management interface. Use a separate "out-of-band" network for administration.
Micro-segmentation with Zero Trust: Don't think of your firewall as the only thing that protects you. Break up your internal network into smaller parts so that if the gateway is hacked, the attacker is stuck in a "DMZ" with no way out.
What Will Edge Resilience Look Like in the Future?
The Cisco ASA/FTD zero-day crisis of 2026 is a very important reminder that the gatekeeper is the most wanted person. We need to be more aggressive in how we check and keep an eye on our infrastructure as attackers get better at living on our hardware.
Hoplon Insight: Edge devices are no longer just walls that don't do anything; they can be used as weapons by someone who knows how to use them. In 2026, security isn't something you set up once and forget about. It's a constant cycle of monitoring, patching, and forensic hunting.
Last Step: Have you checked your Cisco firmware signatures in the last 24 hours? If not, your perimeter may already be broken.