Fake Homebrew Website Attack: How Mac Malware Campaigns Target Developers
Last Updated: November 5, 2026
Key Takeaways
- Attackers have created fake Homebrew websites to trick macOS users into running malicious Terminal commands.
- Some campaigns used Google Ads to redirect users to lookalike websites.
- Other fake pages manipulated clipboard contents, so users copied commands different from what they saw.
- Researchers have linked separate campaigns to AMOS, Odyssey, Cuckoo, and MacSync Stealer.
- These incidents do not establish that the official Homebrew project or its software distribution infrastructure was compromised.
- Verifying the website, checking copied commands, and protecting developer credentials can reduce the risk.
Table of Contents
- What Is the Fake Homebrew Website Attack?
- Why Are Attackers Targeting Homebrew?
- How Fake Homebrew Websites Trick Mac Users
- Documented Fake Homebrew Malware Campaigns
- What Information Can These Infostealers Target?
- Why These Attacks Work
- How to Protect Your Mac From Fake Homebrew Websites
- What Should You Do After Running a Suspicious Command?
- What Security Teams Should Watch For
- Competitor Content Gaps and Additional Insights
- Frequently Asked Questions
- Final Thoughts
What is the Fake Homebrew Website Attack?
A fake Homebrew website attack is a social-engineering technique that tricks macOS users into running malicious commands while believing they are installing legitimate software.
Imagine that you are setting up a development environment on your Mac. You search Google for Homebrew installation instructions, open a page that looks official, and copy the command shown on the screen.
You paste it into Terminal and press Enter.
Everything seems normal. However, the command may contact an attacker-controlled server and run code that was never part of the legitimate Homebrew installation.
This is how several documented campaigns have targeted Mac users.
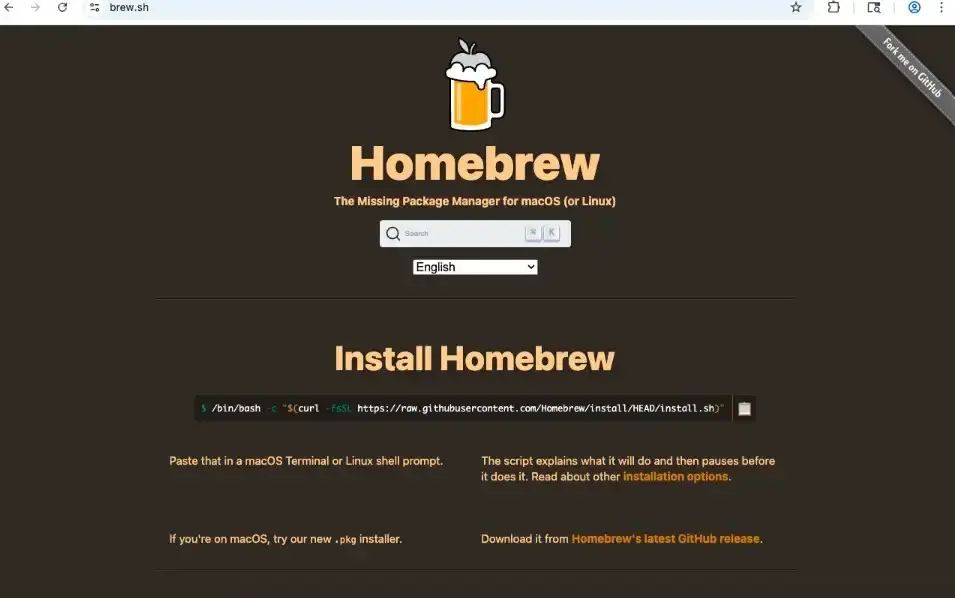
Homebrew is a popular open-source package manager used by developers to install and manage software. Its installation process normally involves running a command in Terminal.
Attackers exploit that familiar workflow.
Instead of finding a vulnerability in Homebrew, they create websites that imitate its appearance and installation instructions. They then persuade visitors to execute commands that deliver malware.
This approach is closely related to ClickFix, a social-engineering technique in which attackers convince users to copy and execute commands themselves.
The important distinction is that a fake Homebrew website does not automatically mean Homebrew itself has been compromised. The documented incidents involve impersonation and malicious instructions delivered through unofficial websites.
Why Are Attackers Targeting Homebrew?
Homebrew is widely used by developers and technical users.
It helps users install command-line tools, development frameworks, libraries, and other software on macOS.
Its normal installation workflow creates an opportunity for attackers.
Consider the steps a developer commonly follows:
- Search for a software installation guide.
- Open the project website.
- Copy the installation command.
- Open Terminal.
- Paste and run the command.
- Continue with the installation process.
These actions are normal in software development.
Attackers do not need to convince users to download an unfamiliar application. They only need to make a malicious command look like a legitimate installation instruction.
That is what makes this technique effective.
A convincing logo, familiar page layout, HTTPS connection, or sponsored search result cannot prove that an installation command is safe.
The security risk comes from the command being executed, not simply from the Homebrew software itself.
How Fake Homebrew Websites Trick Mac Users
Researchers have documented several ways attackers imitate the Homebrew installation experience.
1. Fake Google Ads and Lookalike Domains
One of the earliest widely reported Homebrew-related campaigns appeared in January 2025.
Attackers used a malicious Google advertisement that displayed the legitimate Homebrew website address. However, clicking the advertisement redirected visitors to a lookalike domain:
brewe[.]sh
The extra letter made the address appear similar to the official brew.sh domain.
The fake page copied the familiar Homebrew installation experience and encouraged visitors to run a Terminal command.
Researchers identified Atomic macOS Stealer, also known as AMOS, in connection with this campaign.
This is an example of malvertising. Attackers use online advertisements to direct people toward malicious websites.
The incident also highlights an important point: a sponsored search result is not a guarantee that the destination is trustworthy.
2. Hidden Commands in the Clipboard
A more deceptive technique appeared in a separate investigation published by Iru, formerly Kandji, in October 2025.
Researchers identified multiple fake Homebrew websites that closely copied the official installation page.
One important example was homebrewoneline[.]org.
The fake pages encouraged visitors to use a dedicated Copy button instead of manually selecting the displayed installation command.
That small design choice created an opportunity for clipboard manipulation.
JavaScript on the page could place an attacker-controlled command into the clipboard. As a result, the text copied by the visitor was not necessarily identical to the command visible on the website.
The user believed they had copied a normal Homebrew installation instruction.
In reality, the clipboard could contain additional malicious instructions.
This technique makes the attack more deceptive because the victim may not notice the difference between the displayed text and the copied content.
3. ClickFix-Style Installation Instructions
ClickFix is not limited to fake CAPTCHA pages.
Attackers can adapt the same idea to software installation pages, fake updates, download portals, and other familiar workflows.
In a Homebrew-themed attack, the fake website presents a command as something the visitor must execute to complete an installation.
The user performs the action voluntarily because the page appears legitimate.
This is different from a traditional drive-by download. The attack depends on convincing the victim to execute the instruction.
Microsoft has also documented other macOS ClickFix campaigns that use lookalike websites and browser-based checks to show deceptive instructions to selected visitors.
The broader lesson is that macOS users can be targeted through social engineering even when attackers do not exploit a new operating-system vulnerability.
Documented Fake Homebrew Malware Campaigns
Not every fake Homebrew incident belongs to the same campaign.
Researchers have reported different websites, infrastructure, timelines, and malware families. The following examples should therefore be treated as separate investigations unless a source establishes a connection.
January 2025: Fake Homebrew Advertisement Delivered AMOS
In January 2025, researchers reported a malicious Google advertisement targeting people searching for Homebrew.
The advertisement appeared to show the legitimate brew.sh address but redirected users to brewe[.]sh.
The fake installation page instructed visitors to run a command in Terminal.
Researchers identified Atomic macOS Stealer, also known as AMOS, as the malware associated with this campaign.
AMOS is an information stealer designed to collect sensitive information from infected devices.
The incident demonstrated how attackers could abuse trust in both search advertisements and familiar developer tools.
October 2025: Iru Documented Clipboard Manipulation
In October 2025, Iru published its investigation into spoofed Homebrew installer websites.
Researchers found multiple domains imitating the official Homebrew page.
The investigation highlighted a clipboard manipulation technique that could place hidden commands into the clipboard when visitors clicked a Copy button.
The same infrastructure was associated with Odyssey Stealer activity.
The important finding was not simply that fake Homebrew pages existed. It was that attackers could manipulate the content users copied without making the difference obvious on the page.
This makes checking copied text an important security practice.
October 2025: Hunt.io Reported Broader Fake Developer Tool Campaigns
In a separate investigation published on October 16, 2025, Hunt.io described campaigns targeting users of several developer and software platforms.
The research discussed fake Homebrew, TradingView, and LogMeIn websites.
Researchers connected parts of the activity with AMOS and Odyssey Stealer.
The investigation also described the use of deceptive download pages and clipboard-based techniques.
This report provides broader context for the Homebrew incidents. Attackers were not relying on one software brand. They were impersonating multiple familiar tools used by technical users.
February 2026: Fake Homebrew Domains Delivered Cuckoo Stealer
On February 17, 2026, Hunt.io published another investigation involving fake Homebrew websites.
Researchers identified typosquatted domains that imitated the legitimate Homebrew ecosystem.
The campaign used a ClickFix-style workflow to persuade macOS users to execute a modified installation command.
Hunt.io reported that the activity delivered a credential-harvesting component followed by a second-stage macOS infostealer identified as Cuckoo Stealer.
The investigation described the malware's ability to target sensitive information, including browser credentials, session data, macOS Keychain information, messaging sessions, VPN-related data, and cryptocurrency wallet information.
This was a separate 2026 investigation. It should not be presented as proof that the January 2025 AMOS campaign evolved into Cuckoo Stealer.
May 2026: Fake Homebrew Advertisement Delivered MacSync Stealer
On May 1, 2026, the SANS Internet Storm Center published an investigation by Brad Duncan about a malicious advertisement impersonating Homebrew.
The report described activity observed on April 30, 2026.
The advertisement directed visitors to a fake Homebrew page hosted through Google Sites. The page presented copy-and-paste instructions associated with MacSync Stealer.
This incident is important because it shows that attackers continued using Homebrew as a lure in 2026.
It also demonstrates why blocking only previously reported domains is not enough. New websites and delivery infrastructure can appear later.
Campaign Comparison
|
Reported activity |
Date |
Main delivery method |
Associated malware |
|
Fake Homebrew advertisement |
January 2025 |
Google Ads and lookalike domain |
AMOS |
|
Iru spoofed Homebrew pages |
October 2025 |
Clipboard manipulation |
Odyssey Stealer-associated infrastructure |
|
Hunt.io developer-tool campaign |
October 2025 |
Fake software websites and clipboard manipulation |
AMOS and Odyssey |
|
Fake Homebrew typosquats |
February 2026 |
ClickFix-style installation lure |
Cuckoo Stealer |
|
Fake Homebrew advertisement |
May 2026 |
Malicious advertisement and fake installation page |
MacSync Stealer |
These reports show recurring abuse of the Homebrew installation workflow. They do not establish that every incident involved the same threat actor or infrastructure.
What Information Can These Infostealers Target?
The malware families associated with fake Homebrew campaigns have different capabilities.
However, macOS information stealers commonly seek data that can help attackers access personal accounts, developer platforms, and other online services.
Depending on the malware family and its version, targeted information may include:
|
Data category |
Why attackers may want it |
|
Browser credentials |
Access to websites and online accounts |
|
Authentication cookies |
Potential access to active sessions |
|
macOS Keychain data |
Sensitive information stored by macOS and supported applications |
|
Cryptocurrency wallet information |
Access to valuable digital assets |
|
Developer credentials |
Access to repositories and development platforms |
|
Application data |
Information stored by selected applications |
|
System information |
Details about the infected device |
A developer workstation can contain more sensitive information than an ordinary personal computer.
For example, it may have access to source-code repositories, cloud services, development environments, API credentials, and internal business platforms.
If an infostealer collects valid credentials or active session information, attackers may attempt to use that information to access additional services.
However, an infection does not automatically mean that every account or connected organization has been compromised. The actual impact depends on the information collected, the permissions associated with it, and whether the credentials remain valid.
This is why credential protection is an important part of endpoint security.
Why These Attacks Work
Fake Homebrew websites take advantage of familiar developer behavior.
Developers regularly copy commands from documentation and run them in Terminal. They may also install packages, update dependencies, and configure development tools through command-line instructions.
Attackers make that routine behavior work against the user.
Several factors increase the risk:
Trust in familiar branding: A copied logo and similar page layout can make a fake website look convincing.
Typosquatted domains: A small difference in a website address can be easy to miss.
Sponsored search results: Users may assume that an advertisement has already been checked for safety.
Clipboard manipulation: The copied command may not match the text displayed on the page.
Command-line familiarity: Developers may be comfortable running installation commands without examining every part of them.
Limited visibility: Some malicious pages may show different content depending on the visitor or browser environment.
Microsoft's August 2026 research into macOS ClickFix activity also described browser-fingerprinting techniques used to control which visitors received deceptive content.
This can make automated analysis more difficult because a security scanner and a real macOS visitor may not receive the same page.
The central lesson is straightforward: a familiar installation process does not make every command trustworthy.
How to Protect Your Mac From Fake Homebrew Websites
Protecting against fake Homebrew attacks requires more than recognizing one malicious domain.
Users and organizations should verify software sources, examine installation instructions, and protect sensitive credentials.
1. Use the Official Homebrew Website
The official Homebrew website is:
Homebrew also publishes its installation documentation through its official documentation site:
Homebrew Installation Documentation
Use these official resources rather than websites that imitate the Homebrew brand.
Do not assume a website is legitimate simply because its domain contains words such as Homebrew, brew, Mac, or install.
Check the complete domain before following its instructions.
2. Review Installation Commands Before Running Them
Terminal commands can download files, run scripts, and change system settings.
Before executing an installation instruction, check its source and understand what it is expected to do.
Pay attention to:
- The website or server providing the installation files.
- Whether the command downloads content from an unfamiliar domain.
- Whether downloaded content is executed immediately.
- Whether the command contains unexpected encoded or unreadable sections.
- Whether it requests permissions that do not match the task.
You do not need to understand every technical detail of a script before deciding to investigate it further.
If a command comes from an unfamiliar website or contains unexpected behavior, stop and verify it through the official project's documentation.
3. Check Clipboard Contents
The Iru investigation demonstrated why users should not blindly trust a webpage's Copy button.
A page may display one command while copying different content to the clipboard.
For sensitive installation instructions, compare the copied text with the command provided by the official project.
If the page prevents normal text selection or insists that you use a particular Copy button, treat that behavior as a warning sign.
Do not execute a command simply because the website says it is required.
4. Treat Sponsored Search Results Carefully
A paid advertisement is not proof that a website is safe.
The January 2025 and May 2026 Homebrew-related reports show how malicious advertisements can direct users to fake installation pages.
Instead of relying on the advertisement's displayed address, verify the destination before entering information or running commands.
Security-conscious users should also avoid assuming that an advertisement has been reviewed for every possible malicious behavior.
5. Protect Developer Credentials
Development devices may store credentials that provide access to important services.
Organizations should reduce the amount of sensitive information available on individual workstations.
Useful practices include:
- Avoid storing unnecessary long-lived credentials on developer devices.
- Use separate credentials for development and production.
- Apply least-privilege access.
- Use strong authentication and multifactor authentication where supported.
- Rotate exposed credentials after a suspected compromise.
- Revoke sessions and tokens that may have been accessed by an attacker.
These measures can limit the damage if an information stealer compromises a workstation.
6. Use Endpoint Security
Endpoint security can help organizations identify suspicious activity on developer devices.
Security teams should pay attention to unexpected script execution, suspicious downloads, unusual process behavior, and attempts to access sensitive information.
Endpoint protection can provide another layer of defense, but it cannot guarantee that every social-engineering attack will be stopped.
For organizations that need stronger endpoint visibility and protection, Hoplon InfoSec's Endpoint Security services can be considered as part of a broader security strategy.
7. Train Developers to Recognize ClickFix
Traditional security awareness training often focuses on suspicious emails and attachments.
Developer-focused training should also cover:
- Fake software installation pages.
- Typosquatted domains.
- Malicious search advertisements.
- Clipboard manipulation.
- Fake CAPTCHA and ClickFix instructions.
- Untrusted command-line installation scripts.
- Credential-stealing malware.
Developers should understand that an installation command is still executable code, even when it appears on a professional-looking website.
8. Monitor Threat Intelligence
Security teams should monitor relevant threat intelligence for newly reported fake domains, malware families, and delivery techniques.
Indicators of compromise can support investigations and help security teams identify known malicious activity.
However, domain names and file hashes can change. Blocking a previously reported indicator does not guarantee protection from a new campaign.
Behavior-based monitoring and endpoint investigation should complement indicator-based detection.
What Should You Do After Running a Suspicious Command?
If you believe you have executed a malicious Homebrew installation command, treat the device as potentially compromised.
Do not assume that closing Terminal or deleting the downloaded file has resolved the issue.
Consider these defensive steps:
- Stop using the affected device for sensitive activities. Avoid accessing important accounts or services from it until the situation has been assessed.
- Contact your IT or security team. If the Mac belongs to an organization, report the incident through its approved security process.
- Preserve relevant information. Keep the suspicious website address, approximate time, and any available security alerts for investigation.
- Use trusted security support. Have the device assessed with reputable endpoint security tools or by a qualified incident-response professional.
- Review account activity from a trusted device. Check for unusual sign-ins and unexpected account changes.
- Revoke potentially exposed sessions and credentials. Change affected passwords and rotate exposed tokens or API credentials from a trusted device.
- Follow the organization's recovery process. The appropriate cleanup or device-rebuild decision depends on the investigation findings.
For business devices, security teams should also review whether the affected Mac had access to source-code repositories, cloud accounts, internal systems, or production credentials.
The response should address both the infected device and any credentials or services that may have been exposed.
What Security Teams Should Watch For
Security teams should not rely only on a list of known fake Homebrew domains.
Attackers can change domains, replace malware payloads, and modify installation pages.
A more useful defensive approach combines threat intelligence with endpoint and account monitoring.
|
Area to monitor |
Defensive purpose |
|
Unusual Terminal activity |
Identify unexpected command execution |
|
Downloads from unfamiliar websites |
Investigate suspicious file retrieval |
|
Unexpected child processes |
Find unusual relationships between applications and scripts |
|
Credential-access alerts |
Identify possible information-stealing behavior |
|
New or unusual background activity |
Investigate unexpected software behavior |
|
Suspicious outbound connections |
Review possible communication with malicious infrastructure |
|
Unusual account sign-ins |
Identify possible misuse of exposed credentials |
|
Developer platform activity |
Check for unexpected repository or cloud access |
Organizations should also review developer workstation security policies.
A developer device should not have unrestricted access to every business resource simply because its user needs development tools.
Separating development and production access can reduce the impact of a compromised workstation.
Frequently Asked Questions
Is the official Homebrew website compromised?
The campaigns discussed in this article involved fake websites and impersonated installation instructions. The cited investigations do not establish that the official Homebrew website or its project infrastructure was compromised.
Always use the official website at brew.sh.
What is the fake Homebrew malware?
Fake Homebrew malware refers to malicious software distributed through websites that impersonate Homebrew. Researchers have associated separate campaigns with AMOS, Odyssey Stealer, Cuckoo Stealer, and MacSync Stealer.
These are different malware families or reported campaign associations, not one single Homebrew malware.
What is Homebrew ClickFix?
Homebrew ClickFix describes a social-engineering approach in which a fake Homebrew page persuades a user to copy and execute a malicious command in Terminal.
The technique exploits user trust rather than necessarily exploiting a vulnerability in macOS.
Can a fake Homebrew website steal passwords?
Yes. Some campaigns associated with fake Homebrew websites delivered information stealers designed to collect credentials and other sensitive information.
The exact data targeted depends on the malware family and its version.
Can Google Ads lead to fake Homebrew websites?
Yes. Researchers documented Homebrew-related malvertising incidents in January 2025 and May 2026.
These reports demonstrate that sponsored search placement should not be treated as proof of website authenticity.
Is macOS safe from infostealer malware?
macOS includes security protections, but no operating system is completely immune to malware or social engineering.
Users can still be tricked into executing malicious commands or installing untrusted software.
How can I verify a Homebrew installation command?
Start with the official Homebrew website and installation documentation. Compare any command you receive with the instructions published by the official project.
Do not execute commands from unfamiliar websites simply because they look similar to the official installation instructions.
What should developers do if they suspect a Homebrew infection?
Stop using the affected device for sensitive work, contact the appropriate security team, and investigate possible credential exposure.
Potentially exposed passwords, sessions, API keys, and other credentials should be reviewed and revoked or rotated from a trusted device.
Final Thoughts
Fake Homebrew websites show how attackers can turn an ordinary developer workflow into a malware delivery opportunity.
A user searches for a trusted tool, opens a convincing page, copies an installation command, and runs it in Terminal. The process looks familiar, but the command may come from an attacker-controlled source.
Researchers have documented different campaigns using this approach, with malware families including AMOS, Odyssey, Cuckoo, and MacSync Stealer.
The incidents do not prove that the official Homebrew project was compromised. Instead, they highlight the risks of trusting unofficial websites and executing commands without checking their source.
For developers and organizations, the lesson is simple: verify installation instructions, inspect copied commands, protect credentials, and monitor developer endpoints.
A few seconds of verification can prevent a routine software installation from becoming a serious security incident.
About Hoplon InfoSec
Hoplon InfoSec helps organizations strengthen their cybersecurity posture through services such as Endpoint Security, penetration testing, and security monitoring. Learn more about its cybersecurity services or contact the team.
Editorial and Fact-Checking Note
This article distinguishes between separate investigations and does not assume that all fake Homebrew campaigns share the same operators or infrastructure. Malware capabilities are described at a high level because they can vary by family and version.
Hoplon Infosec’s Endpoint Security can protect macOS users from threats like Homebrew spoofed websites. By detecting suspicious scripts, clipboard injections, and unusual activity in real time, they help prevent attacks before damage occurs.
Follow us on X (Twitter) and LinkedIn for more cybersecurity news and updates. Stay connected on YouTube, Facebook, and Instagram as well.