
Penetration Testing: Process, Benefits, Tools and Risks
Firewalls, antivirus software, endpoint protection, and other security controls remain essential, but they cannot answer one critical question on their own:
What could an attacker actually do if they targeted your environment today?
That is where penetration testing becomes valuable.
Penetration testing, often called ethical hacking, is an authorized security assessment in which trained professionals simulate realistic attack techniques against networks, applications, systems, APIs, cloud environments, or other approved assets.
The goal is not to cause damage. It is to identify weaknesses, determine whether they can actually be exploited, understand their business impact, and help the organization fix them before a real attacker finds the same path.
NIST describes penetration testing as one of several technical security assessment methods organizations can use to identify vulnerabilities and evaluate security controls. (csrc.nist.gov)
For organizations that want hands-on assessment rather than scanner-only results, Hoplon InfoSec's penetration testing services are designed around controlled attack simulation, manual validation, and remediation guidance.
What Is Penetration Testing?
Penetration testing is a structured and authorized attempt to identify and exploit security weaknesses within a defined scope.
A penetration tester may use many of the same techniques an attacker would use, but under agreed rules, technical boundaries, and business constraints.
A typical engagement may test:
- Networks and servers
- Web applications
- APIs
- Mobile applications
- Cloud environments
- Authentication systems
- Access controls
- Security configurations
- Employee-facing attack surfaces
- Segmentation and trust relationships
The key difference between penetration testing and ordinary security scanning is validation.
A vulnerability scanner may report that a weakness appears to exist. A penetration tester investigates whether that weakness is actually exploitable, what access it provides, and whether it can be combined with other weaknesses to create a more serious attack path.
That difference is explained in more detail in Hoplon's guide to penetration testing vs. vulnerability assessment.
Penetration Testing vs. Vulnerability Assessment
The terms are often used together, but they answer different questions.
|
Area |
Vulnerability Assessment |
Penetration Testing |
|
Main goal |
Discover weaknesses |
Validate realistic attack paths |
|
Automation |
Heavily used |
Automation plus manual testing |
|
Exploitation |
Usually limited or absent |
Controlled exploitation may be performed |
|
Coverage |
Broad |
Usually narrower but deeper |
|
False positives |
May require significant validation |
Findings are typically manually verified |
|
Business impact |
Often inferred |
Can demonstrate realistic impact |
|
Frequency |
Often continuous or recurring |
Usually periodic or event-driven |
|
Output |
List of weaknesses |
Validated findings, attack paths, impact and remediation |
A vulnerability assessment asks:
“What weaknesses exist?”
A penetration test goes further:
“Which of those weaknesses can actually be used, and what could an attacker reach?”
Both have value. In mature security programs, they usually complement each other rather than compete.
Continuous discovery and remediation can be handled through a broader vulnerability management program, while penetration testing provides deeper validation at selected points in time.
The Core Phases of Penetration Testing
There is no single universal workflow used by every provider, but professional penetration tests generally follow a structured methodology.
NIST SP 800-115 organizes technical security assessment around planning, execution, analysis, and post-testing activities, while other methodologies provide more detailed phases. (csrc.nist.gov)
A practical penetration testing engagement commonly includes the following stages.
1. Scoping, Planning, and Rules of Engagement
A professional penetration test should begin before any scanning or exploitation takes place.
The organization and testing team first define:
- Systems that may be tested
- Systems that must not be touched
- Approved testing dates
- Testing hours
- Permitted techniques
- Accounts or credentials that may be provided
- Whether phishing or social engineering is allowed
- Restrictions on denial-of-service testing
- Data-handling requirements
- Emergency contacts
- Stop conditions
This stage is essential because penetration testing involves intentionally interacting with production systems in ways normal users do not.
A clearly defined scope protects both the organization and the testers.
It also prevents a common mistake: running aggressive security tools without understanding the systems behind them.
2. Reconnaissance, Discovery, and Enumeration
After the scope is agreed, testers begin gathering information about the approved targets.
Depending on the engagement, they may identify:
- Live hosts
- Domains and subdomains
- Open ports
- Running services
- Software versions
- Login interfaces
- APIs
- Cloud resources
- Publicly exposed services
- Authentication methods
- Network architecture
- Potential trust relationships
Tools such as Nmap may assist with host and service discovery, while application testing may involve proxying and inspecting application traffic.
Reconnaissance helps testers understand the attack surface before attempting exploitation.
3. Vulnerability Analysis
The next stage combines automated discovery with manual investigation.
Testers may use vulnerability scanners, application security tools, configuration analysis, and manual techniques to identify possible weaknesses.
Examples include:
- Missing security patches
- Unsafe configurations
- Weak authentication
- Broken access controls
- Exposed management interfaces
- Injection vulnerabilities
- Insecure APIs
- Default credentials
- Weak encryption
- Excessive privileges
- Vulnerable software
- Business-logic flaws
This stage should not be confused with simply running a scanner.
Automated tools are useful for coverage and speed, but scanner output normally needs to be validated before it becomes a reliable penetration-test finding.
4. Controlled Exploitation
Once a potential weakness is identified, testers may attempt to exploit it within the authorized scope.
The objective is to determine what a real attacker could accomplish.
A successful test might demonstrate that an attacker could:
- Gain unauthorized access
- Bypass authentication
- Access sensitive information
- Execute commands
- Escalate privileges
- Take over another account
- Reach restricted systems
- Move between approved network segments
Testing should remain controlled.
A professional penetration tester does not need to destroy data or interrupt a business-critical system merely to prove that a vulnerability exists.
The evidence should be sufficient to demonstrate risk without creating unnecessary operational damage.
5. Post-Exploitation and Attack-Path Validation
When permitted by the rules of engagement, testers may examine what becomes possible after initial access.
This could include evaluating:
- Privilege escalation
- Credential exposure
- Internal trust relationships
- Lateral movement opportunities
- Access to sensitive assets
- Segmentation weaknesses
- Detection and alerting behavior
The purpose is not to achieve maximum compromise for its own sake.
The purpose is to understand how one weakness could develop into a larger security incident.
For much broader adversary simulations involving people, processes, detection, and response, organizations may instead need red teaming. Red teaming and penetration testing overlap in some techniques, but they are not identical services.
6. Reporting, Remediation, and Retesting
A penetration test has limited value if the final result is simply a long list of technical issues.
A useful report should explain:
- What was tested
- How testing was performed
- What vulnerabilities were validated
- How each weakness could be exploited
- Evidence supporting the finding
- Systems affected
- Technical impact
- Business impact
- Risk priority
- Recommended remediation
- Any attack paths discovered
Remediation should then be assigned to the appropriate technical teams.
After important issues are fixed, retesting can confirm whether the vulnerability has actually been removed.
This final validation closes the gap between “we changed something” and “we verified that the weakness is no longer exploitable.”
Tools Commonly Used in Penetration Testing
Professional testers normally use a combination of commercial tools, open-source tools, custom scripts, and manual analysis.
Nmap
Nmap is commonly used for network discovery, port scanning, service identification, and mapping exposed network services.
Nessus
Nessus is a vulnerability scanner that can help identify known vulnerabilities, missing patches, and configuration issues.
Its output can support penetration testing, but scanner findings still require interpretation and validation.
Burp Suite
Burp Suite is widely used for web application and API security testing.
It can help testers intercept, inspect, modify, and replay web traffic while investigating issues such as authentication flaws, access-control weaknesses, and input-validation problems.
Web applications require particularly deep manual testing because many business-logic vulnerabilities cannot be reliably discovered by automated scanners.
Hoplon's web application security testing service combines automated coverage with hands-on testing for issues such as broken access control, injection vulnerabilities, authentication weaknesses, and business-logic flaws.
Metasploit
Metasploit provides a framework for security testing and controlled exploitation of known vulnerabilities.
Like any exploitation tool, it should only be used against systems for which explicit authorization has been granted.
Manual Testing Techniques
Tools provide speed, but skilled testers provide context.
Manual penetration testing may include:
- Authentication testing
- Authorization testing
- Business-logic analysis
- Privilege escalation
- Session-management testing
- Access-control bypass attempts
- Configuration review
- API manipulation
- Chaining multiple weaknesses
- Custom scripts
- Credential and trust analysis
Social engineering can also be included in certain assessments, but only when explicitly authorized in the scope.
This is one reason a penetration test should not be reduced to “running a scanner.”
Automation is excellent at identifying patterns. Human testers are better at understanding unusual workflows, combining weaknesses, and asking how an attacker could use several small problems together.
Web, Mobile, Network, and Cloud Penetration Testing
Penetration testing is not one single type of assessment.
The scope should reflect the technology and business risk involved.
Network Penetration Testing
Network testing focuses on systems such as:
- Servers
- Firewalls
- VPN gateways
- Network services
- Internal infrastructure
- Remote-access systems
- Network segmentation
Web Application Penetration Testing
Web testing focuses on vulnerabilities including:
- Broken access control
- Authentication problems
- Injection attacks
- Session-management flaws
- Business-logic weaknesses
- Sensitive data exposure
- Security misconfiguration
The OWASP Web Security Testing Guide provides a detailed framework for testing web applications and web services. (owasp.org)
Mobile Application Testing
Mobile applications introduce additional attack surfaces involving:
- Local data storage
- Mobile APIs
- Runtime behavior
- Application permissions
- Authentication tokens
- Reverse engineering
- Cryptography
- Device-specific security controls
Organizations developing Android or iOS applications may therefore need dedicated mobile application security testing alongside infrastructure testing.
Cloud and SaaS Testing
Cloud-focused testing may examine:
- Identity and access management
- Excessive permissions
- Exposed storage
- Misconfigured services
- Cloud APIs
- Secrets
- Publicly accessible resources
- Trust relationships between services
The testing approach should always reflect the provider's rules and the organization's authorized scope.
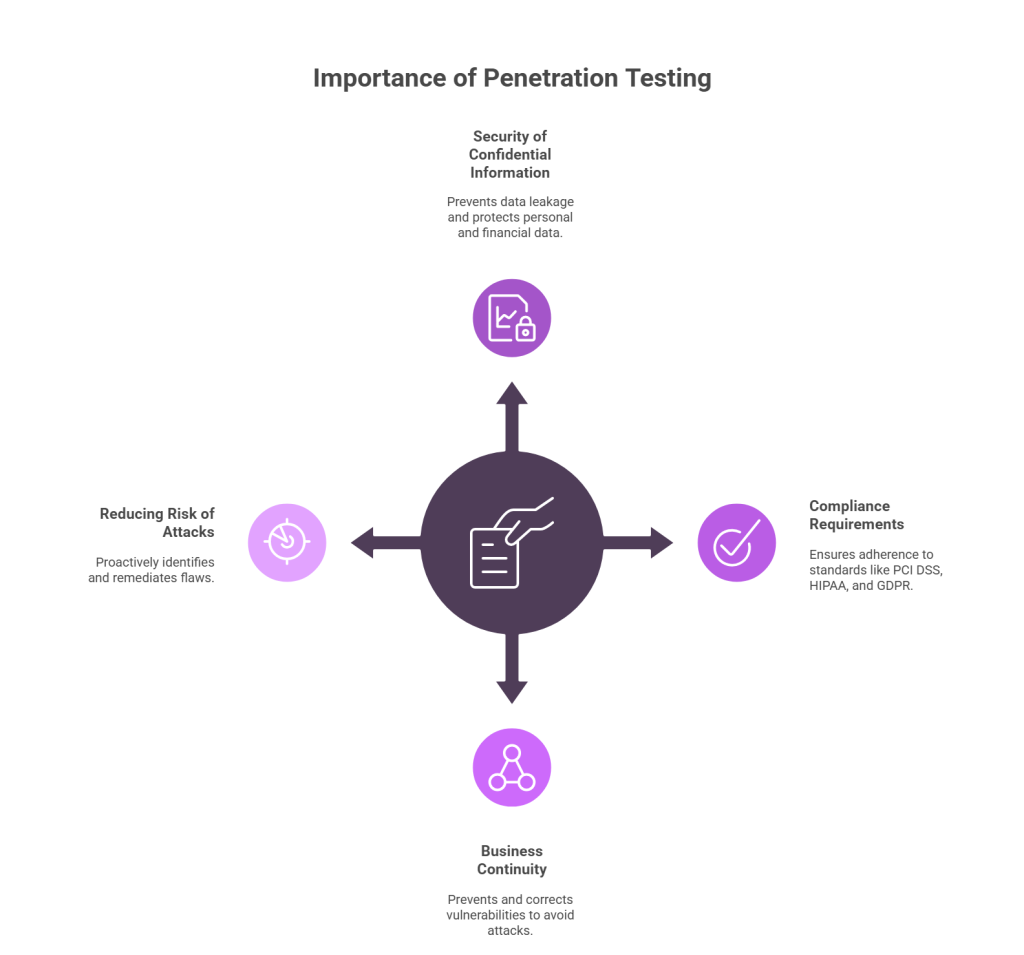
Why Businesses Need Penetration Testing
Modern businesses depend on interconnected applications, identities, endpoints, cloud services, APIs, and third-party platforms.
Each connection creates another place where a security weakness could appear.
Penetration testing helps organizations understand which weaknesses represent practical risk.
1. Identify Exploitable Weaknesses
A vulnerability may exist without being realistically exploitable.
Penetration testing helps determine which weaknesses create genuine attack paths.
2. Validate Security Controls
Organizations invest in:
- Firewalls
- Endpoint protection
- Authentication controls
- Network segmentation
- Monitoring systems
- Web application firewalls
- Access controls
A penetration test provides an opportunity to determine whether those controls behave as expected when exposed to realistic attack techniques.
Endpoint controls remain particularly important after the assessment. Hoplon's guide to modern endpoint security explains how prevention, detection, containment, and response complement point-in-time security testing.
3. Protect Sensitive Data
A successful penetration test may reveal attack paths leading toward:
- Customer information
- Financial records
- Business data
- Internal systems
- Intellectual property
- Authentication credentials
Finding that path during an authorized assessment allows an organization to close it before a malicious actor discovers it.
4. Improve Risk Prioritization
Not every vulnerability deserves the same response.
A technically serious vulnerability on an isolated system may create less immediate business risk than a smaller weakness that exposes an internet-facing authentication system.
Penetration testing gives security teams evidence they can use when deciding what to fix first.
5. Support Business Continuity
Some security weaknesses can lead to ransomware, unauthorized access, system disruption, or data theft.
Testing critical systems can reveal where defensive gaps could turn into operational problems.
6. Improve Detection and Response
Depending on the engagement, security teams may compare penetration-test activity with:
- EDR alerts
- SIEM logs
- IDS/IPS alerts
- Authentication logs
- SOC detections
If a tester completes an important attack step without generating the expected alert, the organization has learned something valuable about its detection coverage.
Penetration Testing and Compliance
Penetration testing can support regulatory and compliance programs, but the requirements should be described carefully.
PCI DSS
PCI DSS is one of the clearest examples.
Under PCI DSS v4.x, Requirement 11.4 covers regular internal and external penetration testing and requires organizations to address exploitable vulnerabilities and security weaknesses found during testing. (pcisecuritystandards.org)
The PCI Security Standards Council also publishes detailed penetration-testing guidance covering scope, methodology, tester qualifications, application and network testing, and reporting. (listings.pcisecuritystandards.org)
HIPAA
HIPAA requires covered organizations to perform security risk analysis and implement appropriate safeguards.
However, it would be inaccurate to say that HIPAA universally requires every organization to perform a specific penetration test on a fixed schedule.
Penetration testing may form part of a broader healthcare security-assessment program depending on the organization's risks, controls, and compliance approach.
GDPR
GDPR similarly should not be described as imposing a universal annual penetration-testing requirement.
Article 32 requires appropriate technical and organizational security measures and includes a process for regularly testing, assessing, and evaluating the effectiveness of security measures.
Penetration testing can support that objective, but the appropriate testing program depends on the organization's circumstances.
This distinction is important: penetration testing can provide valuable compliance evidence without being a universal requirement under every regulation.
The Role of Penetration Testing Teams
Organizations can use different testing models depending on their size, technical capabilities, and independence requirements.
Internal Security Teams
Internal teams understand the environment well and may conduct recurring assessments or targeted testing.
Their familiarity with architecture can make them highly effective at identifying technical weaknesses.
External Penetration Testers
Independent providers offer a different perspective.
They may discover weaknesses that internal teams overlook because they approach the environment without the same assumptions.
External testing can also be useful when customers, auditors, or business partners require independent evidence.
Red Teams
Red teams typically conduct broader, goal-oriented adversary simulations.
Instead of focusing only on individual vulnerabilities, they may test whether an organization can detect and stop a realistic attacker moving across people, processes, endpoints, identities, and infrastructure.
Benefits of Penetration Testing
A properly scoped penetration test can provide several practical benefits.
Early Discovery of Security Weaknesses
Problems can be found before attackers use them.
Real-World Validation
Testing demonstrates which weaknesses can move beyond theoretical scanner findings.
Better Remediation Priorities
Security teams can focus resources on vulnerabilities with demonstrated impact.
Stronger Infrastructure
Findings can improve network architecture, access control, application security, and configuration standards.
Better Security Awareness
Organizations gain a clearer view of how attackers could approach their systems.
Evidence for Audits and Customers
Testing reports and remediation records may provide useful evidence during security reviews, customer assessments, and certain compliance activities.
Continuous Security Improvement
Lessons from one penetration test can improve future development, architecture, monitoring, and security processes.
Limitations of Penetration Testing
Penetration testing is valuable, but it is not a complete security program.
A Penetration Test Is a Point-in-Time Assessment
The environment may change immediately after testing.
New code, cloud services, employees, vulnerabilities, and configurations can introduce new risk.
That is why penetration testing works best alongside continuous vulnerability management and monitoring.
Scope Limits What Can Be Found
A tester cannot reasonably discover a vulnerability in a system that was excluded from the agreed scope.
Incomplete asset inventories can therefore reduce assessment coverage.
Testing Cannot Guarantee Complete Security
No legitimate penetration tester should promise that an environment is “100% secure” after an assessment.
The test provides evidence about the systems, techniques, and attack paths examined during a defined period.
Automation Cannot Replace Expertise
Scanners are valuable, but they may generate false positives or miss weaknesses involving complex workflows and business logic.
Experienced testers add validation, judgment, creativity, and context.
Penetration Testing Does Not Replace Detection and Response
Organizations still need:
- Security monitoring
- Endpoint protection
- Incident response
- Vulnerability management
- Patch management
- Identity protection
- Secure software development
- Backups and recovery planning
Testing tells you where defenses break. Operational security controls are what protect the organization every day.
How Often Should Penetration Testing Be Performed?
There is no single frequency that is correct for every organization.
Testing frequency should reflect factors such as:
- Regulatory requirements
- System criticality
- Exposure to the internet
- Frequency of application releases
- Infrastructure changes
- Previous findings
- Customer requirements
- Threat profile
- Business risk
Organizations commonly consider additional testing after significant changes such as:
- Major application releases
- New infrastructure
- Cloud migrations
- Authentication redesigns
- Network segmentation changes
- Major mergers or integrations
Compliance frameworks may impose their own specific schedules, so organizations should follow the requirements that actually apply to them.
What Should a Good Penetration Testing Report Include?
A useful report should help both technical teams and business stakeholders understand the findings.
Look for:
- Executive summary
- Scope
- Methodology
- Testing dates
- Systems tested
- Findings
- Evidence
- Exploitation details
- Risk ratings
- Business impact
- Technical remediation
- Attack paths
- Limitations
- Retest results
Raw scanner output is not a penetration-testing report.
The real value comes from explaining what can be exploited, why it matters, and what should be fixed first.
Conclusion
Penetration testing gives organizations something ordinary security tools cannot provide on their own: evidence of how their defenses behave when someone actively looks for a way around them.
It combines technical tools, manual analysis, controlled exploitation, and real-world attack thinking to identify vulnerabilities and demonstrate their practical impact.
But penetration testing should not operate in isolation.
The strongest security programs combine penetration testing with vulnerability management, endpoint protection, secure development, monitoring, incident response, and regular remediation.
For businesses, financial organizations, healthcare providers, SaaS companies, and other organizations responsible for important systems or sensitive information, the objective is not simply to pass a security test.
It is to understand:
Where could an attacker get in? What could they reach? Would our controls stop them? And what should we fix before they get the chance?
A well-scoped penetration test helps provide those answers.