
Inside Zero-Day Exploit Marketplaces: How the Trade Works in 2026
Last Updated: September 2026
Zero-day exploit marketplaces are markets where previously undisclosed or unpatched software vulnerabilities, exploit code, and sometimes complete attack capabilities are exchanged between researchers, brokers, governments, surveillance companies, security firms, and criminal actors.
The important point is that there is no single "zero-day marketplace."
The ecosystem includes legitimate vulnerability disclosure programs, private commercial exploit brokers, government procurement channels, commercial surveillance vendors, and underground criminal sellers. Their buyers, rules, prices, and motives can be very different.
For businesses, the practical question is not how to participate in this market. It is what the existence of this market means for systems that may have no patch available when an attack begins.
Google Threat Intelligence Group reported that it tracked 90 vulnerabilities exploited as zero-days during 2025. Of those, 43, or 48%, affected enterprise technologies.
Google also reported that commercial surveillance vendors accounted for more attributed zero-day exploitation than traditional state-sponsored espionage groups in its 2025 dataset.
You can review Google's official 2025 Zero-Days in Review for the underlying findings and methodology.
Key Findings
Several developments make the zero-day economy especially relevant to organizations:
- Google tracked 90 exploited zero-days during 2025.
- 43 of those vulnerabilities affected enterprise technologies.
- Enterprise and edge infrastructure are increasingly important targets.
- Commercial surveillance vendors have become significant consumers and developers of advanced exploit capabilities.
- Financially motivated actors also use zero-days, although most cybercrime can still rely on cheaper known vulnerabilities.
- Strong patching alone cannot completely address zero-day risk because exploitation may begin before a vendor releases a fix.
The UK's National Cyber Security Centre provides additional context in its Commercial Cyber Proliferation Assessment.
What Exactly Is a Zero-Day Exploit Marketplace?
A zero-day vulnerability is a security weakness that defenders have not yet had a practical opportunity to patch before exploitation begins.
A vulnerability is the weakness.
An exploit is code or a technique that takes advantage of that weakness.
An exploit chain combines multiple weaknesses to achieve a larger objective.
A zero-click exploit can work without meaningful interaction from the victim, making some of these capabilities particularly valuable to sophisticated attackers.
A marketplace emerges when knowledge of a vulnerability or a working exploit becomes commercially valuable.
There Are Several Zero-Day Markets, Not Just One
Treating the entire ecosystem as a single black market creates the wrong picture.
Defensive and Coordinated Disclosure Markets
Security researchers may disclose vulnerabilities directly to vendors, participate in bug bounty programs, or follow coordinated vulnerability disclosure procedures.
The objective is usually to:
- verify the vulnerability
- inform the affected vendor
- allow remediation
- reduce risk to users
- coordinate public disclosure when appropriate
NIST provides structured guidance for organizations through NIST SP 800-216: Recommendations for Federal Vulnerability Disclosure Guidelines.
Commercial and Government-Oriented Exploit Markets
Private brokers may acquire vulnerabilities or complete exploit capabilities from researchers and make them available to selected customers.
Customers may include government organizations, contractors, intelligence services, and commercial surveillance vendors.
These markets can involve:
- technical validation
- exclusivity agreements
- vulnerability research
- exploit development
- buyer vetting
- long-term contracts
Underground Criminal Markets
A separate ecosystem exists around criminal forums, private groups, exploit suppliers, and access brokers.
This market should not automatically be confused with premium government-focused exploit brokerage.
Exploit development can also become specialized. One actor may discover or develop a capability while another actor obtains and deploys it.
For defenders, this specialization matters because attackers do not always need to perform their own vulnerability research.
Who Participates in Zero-Day Exploit Marketplaces?
The ecosystem involves several different types of participants.
Vulnerability Researchers
Researchers discover weaknesses through activities such as:
- fuzzing
- reverse engineering
- source-code review
- application testing
- protocol analysis
- security research
When researchers discover a vulnerability, they may disclose it to the vendor, submit it through a bug bounty program, publish research after coordinated disclosure, or enter another legal commercial arrangement.
Exploit Developers
Finding a vulnerability and turning it into a reliable exploit are different tasks.
An exploit developer may need to understand:
- memory protections
- sandbox boundaries
- authentication controls
- privilege restrictions
- operating system protections
- application behavior
More sophisticated attacks may require several vulnerabilities working together.
Exploit Brokers
Brokers operate between researchers and buyers.
They may:
- evaluate submissions
- validate technical claims
- negotiate terms
- establish exclusivity
- manage customer relationships
- deliver capabilities
Governments and Intelligence Customers
Government organizations have historically been important buyers of offensive cyber capabilities.
Possible purposes include:
- intelligence collection
- national security
- criminal investigations
- military operations
Government involvement creates a difficult security-policy question.
Should a newly discovered vulnerability remain secret for intelligence purposes, or should it be disclosed so the vendor can protect users?
There is no universal answer that applies to every country or case.
Commercial Surveillance Vendors
Commercial surveillance companies can acquire or develop exploit capabilities and integrate them into surveillance platforms.
This part of the market has attracted increasing attention because advanced exploitation capabilities can become available to customers that could not independently develop them.
Criminal Actors
Cybercriminal groups also use exploits, but most financially motivated attackers do not require expensive zero-days.
Known vulnerabilities in unpatched internet-facing systems are often:
- cheaper
- easier to obtain
- easier to scale
- already supported by public exploit information
That is why businesses should not ignore ordinary vulnerability management while focusing on advanced zero-day threats.
A mature risk-based vulnerability management program should address both known vulnerabilities and emerging threats.
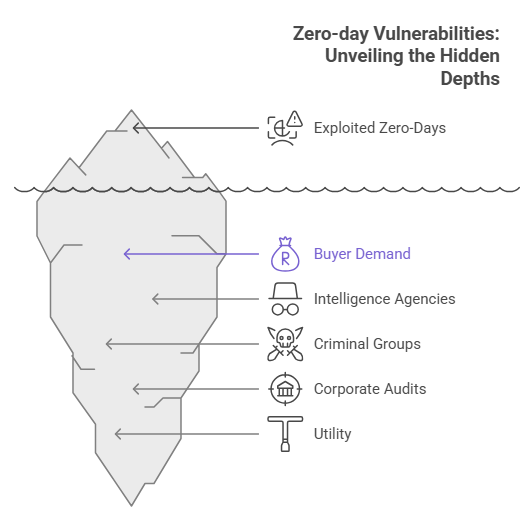
How Are Zero-Day Exploits Valued?
There is no authoritative global price for a zero-day exploit.
The value depends on several factors.
| Factor | Why It Matters |
|---|---|
| Target platform | Widely used or strategically valuable software may attract more interest |
| Remote exploitation | Remote access can increase operational value |
| User interaction | Zero-click exploitation may be more valuable |
| Privilege level | Root, kernel, SYSTEM, or administrator access can increase impact |
| Exploit chain | A complete chain may achieve more than one isolated vulnerability |
| Reliability | Stable exploitation is more useful than an unreliable proof of concept |
| Stealth | Avoiding detection can increase offensive value |
| Exclusivity | Exclusive access can preserve the usefulness of the capability |
| Version coverage | Broader target coverage can increase utility |
| Patch status | Value can fall quickly after disclosure and remediation |
Publicly advertised prices should not automatically be treated as confirmed sale prices.
Private contracts are rarely transparent, which means precise market-wide pricing claims should be treated cautiously.
Why Zero-Click and Full Exploit Chains Are Valuable
Two vulnerabilities can have very different operational value.
One might only crash an application after a user opens a specially created file.
Another might allow an attacker to:
- execute code remotely
- escape an application sandbox
- gain higher privileges
- access sensitive information
Both can technically be vulnerabilities, but their offensive usefulness is very different.
Modern platforms increasingly use:
- sandboxing
- memory protections
- application isolation
- permission controls
- exploit mitigations
Attackers may therefore need several weaknesses working together.
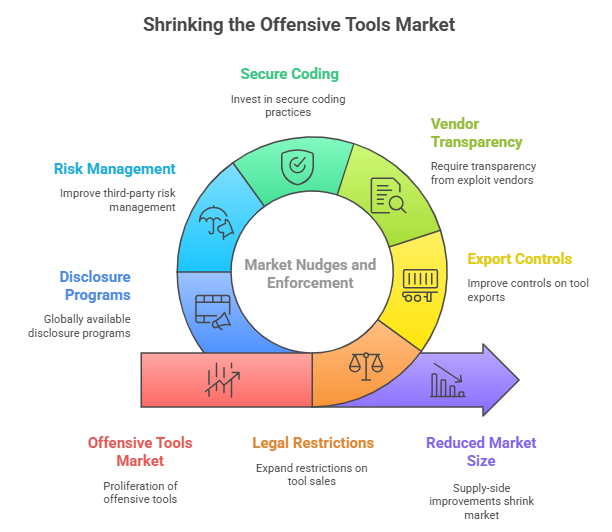
Why Demand Continues Even as Security Improves
Improved product security does not automatically eliminate exploit markets.
In some cases, stronger defenses make successful exploit chains more difficult and expensive to develop.
Buyers may value capabilities that provide:
- access before a patch exists
- reliable exploitation
- low victim interaction
- privileged access
- stealth
- persistence
- exclusivity
- broad platform coverage
At the same time, defensive technology continues to improve.
This creates a constant competition between vulnerability researchers, exploit developers, vendors, defenders, and threat actors.
Enterprise Systems Are Becoming a Bigger Part of the Risk
Enterprise software and edge infrastructure have become increasingly important zero-day targets.
These systems may include:
- VPN gateways
- firewalls
- virtualization systems
- email servers
- security appliances
- identity platforms
- management interfaces
- remote-access infrastructure
These products can be attractive because they may:
- be exposed to the internet
- operate with high privileges
- manage sensitive traffic
- connect multiple internal networks
- provide administrative access
- contain valuable credentials
Organizations should therefore treat edge infrastructure as a high-value asset category.
A broader cyber resilience assessment can help organizations identify weaknesses in security controls, operational readiness, and exposed assets.
The Underground Exploit Supply Chain Is Becoming Specialized
Another important part of the market is specialization.
Attackers do not always discover every vulnerability themselves.
Different actors may specialize in:
- vulnerability discovery
- exploit development
- malware development
- credential theft
- initial access
- infrastructure
- ransomware deployment
- stolen-data sales
This creates a service-based cybercrime ecosystem.
An exploit developer may supply a capability to another attacker who combines it with malware, stolen credentials, compromised infrastructure, or another access method.
Organizations therefore need more than a simple vulnerability list.
Cyber threat intelligence can provide additional context about active threat actors, exploitation trends, campaigns, vulnerabilities, and emerging risks.
AI May Affect Vulnerability Research
AI systems are increasingly being examined for their potential role in:
- vulnerability discovery
- source-code analysis
- reverse engineering assistance
- exploit research
- malware development
- security automation
Claims in this area should be treated carefully.
AI does not automatically make sophisticated zero-day exploitation easy.
Advanced exploit research still requires technical knowledge, target understanding, testing, and operational reliability.
The more important defensive concern is speed.
If attackers can shorten parts of the vulnerability research or exploit-development process, organizations may have less time to react after a vulnerability becomes known.
What Happens When a Zero-Day Is Weaponized?
A vulnerability does not automatically create a complete breach.
A simplified attack lifecycle may look like:
Discovery → Exploit Development → Testing → Acquisition or Sharing → Target Selection → Exploitation → Persistence → Detection → Investigation → Remediation
Defenders can interrupt that process at several stages.
Strong identity controls can restrict attacker movement.
Segmentation can prevent one compromised system from reaching critical infrastructure.
Monitoring can identify abnormal behavior.
Least privilege can limit what compromised accounts can access.
Incident response can contain an attacker before the breach spreads.
The goal is not to predict every unknown vulnerability.
That is impossible.
The goal is to ensure one unknown vulnerability does not automatically provide unrestricted access to the entire organization.
What Should Organizations Do When No Patch Exists?
Zero-day defense requires preparation before the vulnerability becomes public.
1. Know Your Exposed Assets
Maintain an accurate inventory of:
- internet-facing servers
- VPN gateways
- firewalls
- cloud systems
- web applications
- remote-access services
- management interfaces
- edge appliances
If you do not know an asset exists, you cannot protect or prioritize it properly.
2. Follow Official Vendor Advisories
Vendors may release temporary mitigation instructions before a permanent patch becomes available.
Possible mitigations include:
- disabling vulnerable features
- changing configurations
- restricting access
- blocking specific traffic
- removing internet exposure
Always prioritize official vendor instructions for the affected product.
3. Prioritize Active Exploitation
Do not prioritize vulnerabilities using severity scores alone.
Consider:
- evidence of exploitation
- internet exposure
- business importance
- available mitigations
- attacker interest
- privilege level
- potential operational impact
4. Reduce the Attack Surface
If a vulnerable service does not need public internet access, remove the exposure.
Other defensive measures can include:
- restricting administrative interfaces
- disabling unused services
- limiting remote access
- applying network allowlists
- using firewall controls
- reducing unnecessary software
5. Strengthen Identity Security
A zero-day may provide initial access without automatically giving an attacker every permission they need.
Organizations should consider:
- phishing-resistant MFA
- least privilege
- separate administrator accounts
- privileged-access controls
- service-account management
- credential rotation
6. Segment Critical Systems
Do not allow one compromised workstation or edge device to communicate freely with every critical system.
Separate:
- administrative networks
- production infrastructure
- identity systems
- backups
- sensitive databases
- critical business services
7. Improve Logging and Monitoring
Collect available logs from:
- VPN systems
- firewalls
- authentication systems
- identity providers
- DNS
- proxies
- security appliances
- cloud platforms
Longer log retention can also help investigators reconstruct an attack discovered weeks or months later.
8. Test Realistic Attack Paths
Automated vulnerability scanning is useful, but it does not always show what an attacker could accomplish after gaining access.
Authorized infrastructure penetration testing can help organizations evaluate realistic attack paths and control weaknesses.
You can also review the differences between penetration testing and vulnerability assessment when deciding which type of testing is appropriate.
9. Prepare Incident Response Before an Attack
Organizations should decide in advance:
- who can isolate affected systems
- who communicates with vendors
- who preserves evidence
- who handles credential rotation
- how critical systems are restored
- who makes business decisions
- how escalation works
Prepared incident response and recovery procedures reduce the amount of improvisation required during a serious security event.
Can Dark Web Monitoring Detect Zero-Day Activity?
Not every exploit transaction appears on a public or semi-public underground forum.
Many high-value deals may occur through:
- private groups
- encrypted communications
- invitation-only communities
- one-to-one relationships
- private broker networks
That means dark web monitoring cannot guarantee visibility into every zero-day transaction.
It can, however, reveal signals such as:
- exploit advertisements
- stolen credentials
- compromised access
- breach claims
- threat actor discussions
- malware activity
- stolen databases
- company mentions
Organizations concerned about underground exposure can combine deep and dark web monitoring with broader threat intelligence.
Hoplon Infosec also provides a detailed guide explaining what dark web monitoring is and how it works.
Dark web monitoring should be treated as one intelligence source rather than a guarantee that every threat can be discovered.
Ethical and Legal Questions Around Zero-Day Markets
Zero-day markets create a difficult security tradeoff.
Keeping a vulnerability private may preserve its usefulness for intelligence operations.
Disclosing it allows the affected vendor to develop a patch that protects users.
Both decisions can have consequences.
Legal requirements can also vary between jurisdictions.
Relevant issues may include:
- export controls
- sanctions
- computer misuse laws
- authorization
- contracts
- disclosure requirements
- buyer identity
- intended use
Organizations and researchers dealing with specific legal situations should obtain qualified legal advice rather than relying on general cybersecurity guidance.
Why Vulnerability Disclosure Programs Matter
Responsible disclosure programs provide security researchers with a legitimate route for reporting vulnerabilities.
A mature program can provide:
- a clear reporting channel
- testing rules
- defined scope
- coordinated disclosure procedures
- researcher communication
- remediation processes
- rewards where appropriate
Bug bounty programs cannot necessarily compete financially with every commercial exploit buyer.
Their value also comes from creating a predictable and legitimate way for researchers to report weaknesses.
NIST's official Vulnerability Disclosure Guidelines provide useful guidance for organizations building structured disclosure processes.
Commercial Surveillance Has Changed the Risk Model
Commercial surveillance vendors have changed how advanced cyber capabilities can spread.
Instead of every government organization developing advanced exploit capabilities internally, commercial providers may develop or acquire capabilities and make them available to customers.
This can lower the technical barrier for organizations seeking sophisticated intrusion capabilities.
The UK's NCSC discusses this broader market in its official Commercial Cyber Proliferation Assessment.
However, threat modeling still matters.
Not every business faces the same likelihood of being targeted by expensive advanced exploitation.
Higher-risk targets may include:
- government organizations
- journalists
- telecommunications providers
- defense companies
- political organizations
- critical infrastructure
- technology providers
- organizations holding strategically valuable information
Security investment should reflect realistic risk rather than fear.
Why the Market Matters Even If Nobody Buys a Zero-Day Specifically for Your Business
Most businesses will never know whether an exploit used against them came from:
- private research
- a government capability
- an exploit broker
- an underground seller
- a commercial surveillance company
- independent attacker research
That uncertainty does not change the core defensive strategy.
Zero-day markets matter because they:
- create financial incentives for vulnerability discovery;
- allow buyers to obtain capabilities they may not develop themselves;
- support specialized exploit-development ecosystems;
- expand access to sophisticated offensive tools;
- create uncertainty about undisclosed vulnerabilities already being exploited.
The practical defensive response remains straightforward:
- know your assets
- reduce unnecessary exposure
- patch quickly
- prioritize active exploitation
- strengthen identity security
- segment critical infrastructure
- monitor edge devices
- retain useful logs
- test security controls
- maintain incident-response readiness
A valuable zero-day becomes less useful when compromising one system does not automatically give an attacker control over the rest of the environment.
Zero-Day Exploit Marketplaces: The Bottom Line
Zero-day exploit marketplaces are real, but the popular idea of a single secret website where attackers buy undisclosed vulnerabilities is misleading.
The actual ecosystem is fragmented.
It includes:
- independent security researchers
- vulnerability disclosure programs
- bug bounty platforms
- exploit brokers
- government customers
- commercial surveillance vendors
- underground exploit developers
- criminal threat actors
For defenders, knowing exactly where an exploit came from is less important than building systems capable of limiting its impact.
Organizations cannot guarantee that they will detect or prevent every zero-day attack.
They can reduce exposed attack surfaces, strengthen identity controls, segment critical systems, improve detection, test defensive controls, and prepare to contain incidents quickly.
That makes an unknown vulnerability significantly harder to turn into a major business compromise.
If your organization wants a clearer picture of its current cyber risk, Hoplon Infosec can help you assess vulnerabilities, improve visibility, and strengthen your security approach. Explore our cybersecurity services to find the support that best fits your environment.
Follow us on X (Twitter) and LinkedIn for more cybersecurity news and updates. Stay connected on YouTube, Facebook, and Instagram as well. At Hoplon Infosec, we’re committed to securing your digital world. Hoplon Infosec’s Deep and Dark Web Monitoring service helps organizations spot exploit activity, leaks, and emerging threats in hidden marketplaces, giving you the visibility needed to act before attackers do.