Linux KVM Flaw CVE-2026-99312 Exposes AMD Host Memory: What Administrators Need to Know
Can a Virtual Machine Access Memory Outside Its Assigned Environment?
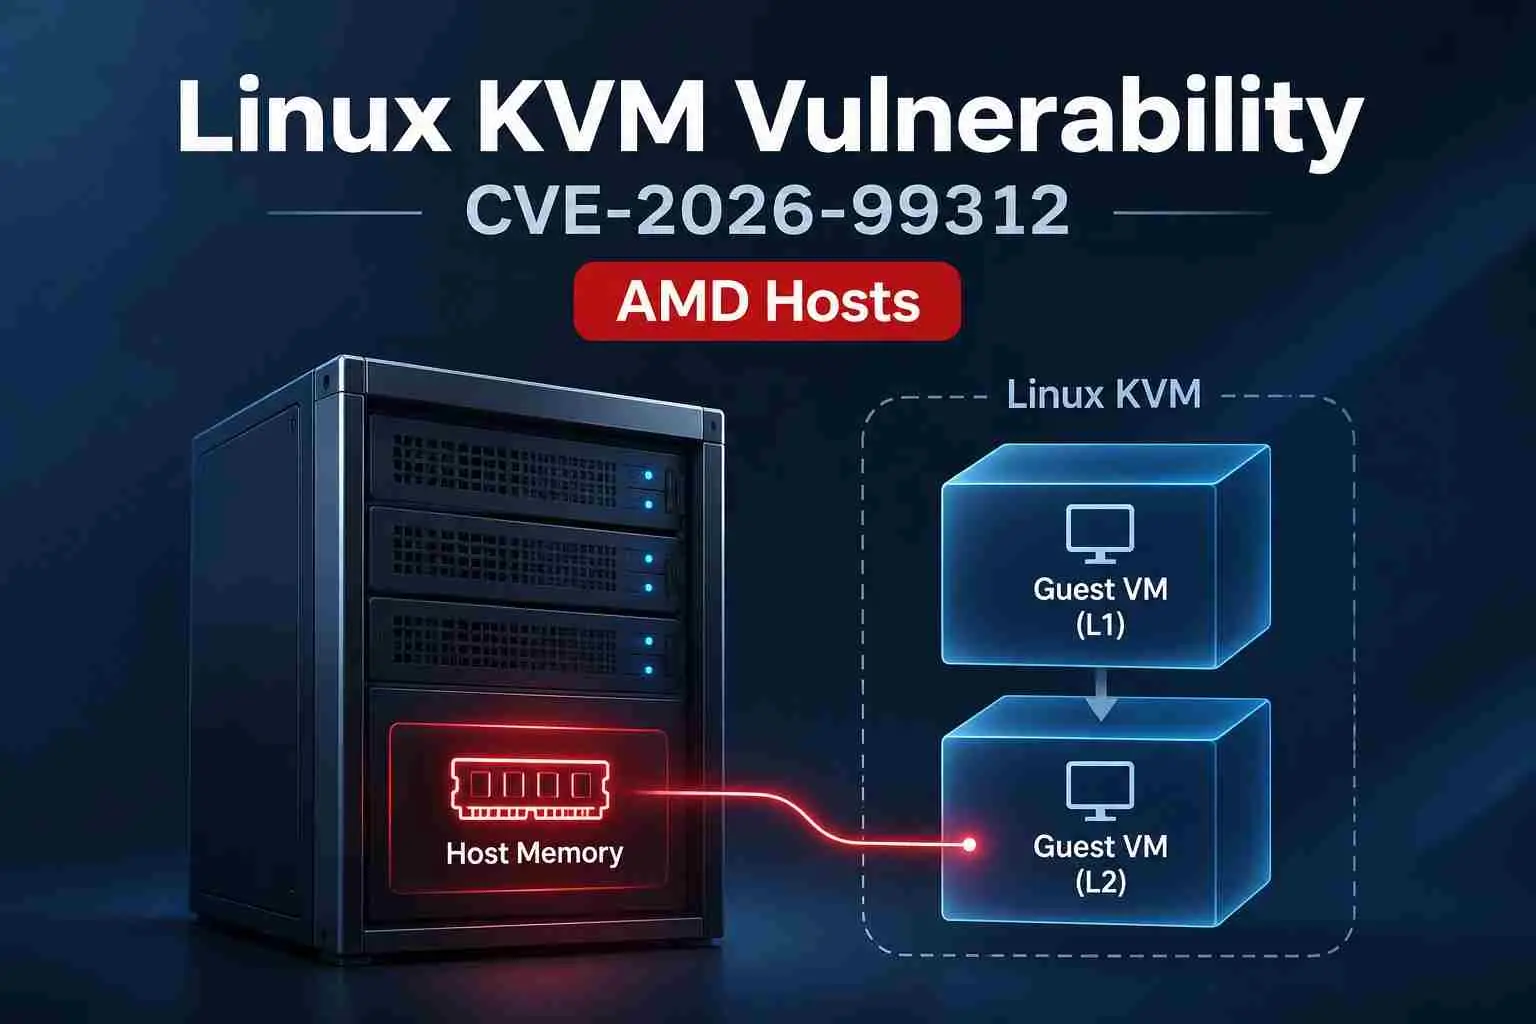
Yes. Security researchers demonstrated that CVE-2026-99312, a Linux KVM vulnerability, can allow a guest virtual machine to access memory belonging to its physical host under specific conditions.
The vulnerability affects AMD-based virtualization environments that support nested virtualization. During authorized research, investigators accessed approximately 127 GB of host memory from a virtual machine running on DigitalOcean infrastructure.
In a separate test on their own physical server, researchers also demonstrated the ability to modify host kernel memory.
DigitalOcean confirmed the findings in its November 19, 2026 disclosure.
The issue challenges a basic security expectation in cloud computing: a virtual machine should not access memory outside the boundaries assigned to it.
For organizations running shared virtualization infrastructure, that boundary is critical.
TL;DR: Key Takeaways
- The vulnerability: CVE-2026-99312 affects Linux KVM memory management during nested virtualization on AMD processors. Under specific conditions, the flaw can expose host memory to a guest VM.
- The demonstrated impact: Researchers accessed approximately 127 GB of host RAM in a cloud environment and demonstrated a separate 32-byte host kernel memory modification on their own server.
- The recommended response: Administrators should identify affected AMD KVM hosts, verify their kernel patch status, and disable nested virtualization where it is unnecessary. Updating the host kernel is the primary remediation.
Table of Contents
- Understanding the Linux KVM Vulnerability
- How the Vulnerability Was Discovered
- How CVE-2026-99312 Works
- Affected Systems and Kernel Versions
- Security Impact on Cloud Infrastructure
- Technical Findings and Real-World Evidence
- How to Check Your Linux KVM Hosts
- How to Mitigate CVE-2026-99312
- Detection and Incident Response
- Frequently Asked Questions
Understanding the Linux KVM Vulnerability
Linux KVM is a virtualization technology built into the Linux kernel. It allows a physical computer to run multiple independent virtual machines.
Each virtual machine operates with its own operating system, applications, and assigned resources.
A single physical server may therefore support many workloads without requiring a separate computer for each one.
Cloud providers use virtualization to allocate computing resources to customers. Organizations also use it to consolidate internal servers, create development environments, and manage infrastructure.
The security of this model depends on isolation.
Although multiple virtual machines share physical hardware, each guest should access only the memory and resources assigned to it.
Why Virtual Machine Isolation Matters
Consider a physical server running several virtual machines.
One VM handles a company's accounting application. Another runs a customer database. A third hosts a development environment.
These systems may use the same physical processor and memory, but they should remain logically separated.
The hypervisor helps enforce that separation.
If a guest VM can bypass the memory controls established by the hypervisor, data belonging to other workloads may become accessible.
That does not automatically mean the data has been stolen.
It means a security boundary that normally prevents unauthorized access may no longer provide the expected protection.
CVE-2026-99312 demonstrates why this distinction matters.
The researchers established that the vulnerability could cross the guest-to-host memory boundary under the tested conditions.
The extent of exposure in any particular production environment depends on its configuration, patch status, and available attack conditions.
Why Nested Virtualization is Important
Nested virtualization allows a virtual machine to run additional virtual machines inside itself.
A simplified environment contains three levels:
|
Level |
Description |
Example |
|
L0 |
Physical host and primary hypervisor |
Linux server running KVM |
|
L1 |
First-level virtual machine |
Customer VM with virtualization access |
|
L2 |
Nested virtual machine |
VM running inside the L1 environment |
Nested virtualization is useful for software development, infrastructure testing, virtualization training, and certain cloud workloads.
However, it also adds complexity to CPU and memory management.
The Linux kernel documentation states that nested virtualization has been enabled by default for supported Intel and AMD KVM configurations since Linux kernel 4.20.
That default does not mean every cloud provider exposes nested virtualization to customers.
Providers can restrict the feature through infrastructure configuration.
How the Vulnerability Was Discovered
The vulnerability was identified by security researcher Oren Yomtov of Terra Security.
The researcher reported the issue through DigitalOcean's bug bounty program.
DigitalOcean investigated the finding and confirmed that the reported behavior affected its infrastructure.
The disclosure followed a coordinated process involving the researcher, cloud provider, and Linux kernel maintainers.
According to the public reporting, Linux KVM maintainers were notified on October 21, 2026.
The mainline correction was merged on November 2, 2026.
Stable kernel fixes were subsequently released, and the CVE was publicly announced on November 18, 2026.
DigitalOcean published its account of the research on November 19.
The Hacker News reported the findings on November 20.
Verified Disclosure Timeline
|
Date |
Event |
|
October 21, 2026 |
Linux KVM maintainers notified |
|
November 2, 2026 |
Mainline kernel fix merged |
|
November 17, 2026 |
Relevant stable kernel releases shipped |
|
November 18, 2026 |
CVE publicly announced |
|
November 19, 2026 |
DigitalOcean published its disclosure |
|
November 20, 2026 |
The Hacker News published its coverage |
These dates establish that the problem was identified and addressed upstream before the wider public reporting.
However, the release of an upstream patch does not prove that every Linux distribution or private virtualization environment has installed it.
System administrators must verify the status of their own infrastructure.
What Makes This Discovery Significant?
The researchers did not simply report a theoretical programming mistake.
They demonstrated memory access across a virtualization boundary.
DigitalOcean confirmed that the research reached approximately 127 GB of host RAM from a guest VM.
The researchers deliberately kept that demonstration read-only.
A separate experiment established that controlled memory modification was also possible on hardware owned by the researchers.
This distinction is important.
The cloud-hosted experiment demonstrated unauthorized memory visibility.
The independent laboratory experiment demonstrated a potential integrity impact.
Together, the findings provide stronger evidence than a vulnerability description based only on a possible system crash.

How CVE-2026-99312 Works
The Linux KVM flaw involves the handling of memory-management state when a processor reset is emulated during nested virtualization.
To understand the problem, it helps to examine how virtual machines access physical memory.
The Role of Memory Translation
A virtual machine uses memory addresses that do not directly identify locations in the host's physical RAM.
The virtualization system translates those addresses into physical memory locations.
AMD processors support this process through nested page tables.
These tables help map guest memory addresses to permitted host memory locations.
Normally, the processor follows translation information maintained by the virtualization system.
This prevents a guest from simply selecting arbitrary physical memory on the host.
CVE-2026-99312 affects the reliability of that translation state.
The Memory Management Unit Problem
The Memory Management Unit, or MMU, manages address translation.
When a virtual CPU changes execution states, KVM must maintain consistent memory mappings.
That includes certain reset operations.
The vulnerability occurs because KVM could fail to reset its MMU context correctly while emulating an INIT processor reset.
INIT is a processor initialization signal.
During the affected operation, KVM could retain memory-management information that should have been refreshed.
The result was a stale memory mapping.
A stale mapping refers to translation information that no longer represents the correct memory state.
Understanding the Stale Pointer
The researchers described a situation in which a pointer continued referencing memory that had already been freed.
A pointer is a value used to identify a memory location.
When software frees memory, that location may later be reused for another purpose.
Continuing to rely on the old pointer can therefore create unpredictable behavior.
This is closely related to a use-after-free condition.
In the affected KVM operation, the processor could continue using a page-table reference after the corresponding memory had been released.
When that memory was reused, its contents could influence subsequent address translation.
Under the conditions demonstrated by the researchers, this allowed memory references outside the guest's permitted allocation.
Why the INIT Reset Matters
The Linux kernel patch addresses how the MMU context is handled during INIT emulation.
Previously, the relevant reset could be skipped when paging was already disabled.
However, the MMU state also tracks whether the virtual CPU is operating in nested guest mode.
Consequently, relying only on the paging state was insufficient.
The correction makes the reset unconditional for the affected operation.
This ensures that stale nested-guest memory-management information is not retained.
The official Linux kernel CVE description identifies the fix as:
KVM: x86: Unconditionally reset MMU context when emulating INIT
The wording describes the correction directly rather than making assumptions about exploitability in every deployment.
Technical Process at a Glance
|
Stage |
Normal Expected Behavior |
Vulnerable Behavior |
|
Nested execution |
L2 guest runs with controlled memory mappings |
Nested execution begins normally |
|
INIT emulation |
KVM refreshes relevant processor state |
MMU context may remain stale |
|
Memory cleanup |
Released memory is no longer referenced |
An old reference may remain active |
|
Memory reuse |
New contents are handled independently |
Reused memory may influence translation |
|
Result |
Guest remains within assigned memory |
Guest may access unintended host memory |
This table explains the failure at a conceptual level.
It is not an exploitation procedure.
The precise outcome depends on processor configuration, kernel behavior, and the state of the nested virtualization environment.
Affected Systems and Kernel Versions
The issue is particularly relevant to Linux virtualization hosts using AMD processors with nested virtualization enabled.
It does not affect every Linux computer.
A desktop computer running Linux without the relevant KVM configuration does not automatically face the demonstrated exposure.
Likewise, an Intel-based KVM environment is not affected by this specific AMD nested virtualization issue, according to Red Hat's advisory.
Configuration-Based Exposure
|
Environment |
Reported Exposure |
|
AMD KVM host with affected code and nested virtualization enabled |
Potentially vulnerable |
|
AMD KVM host with nested virtualization disabled |
Demonstrated attack path unavailable |
|
Intel-based KVM host |
Not affected by this specific issue |
|
Linux system without the affected KVM functionality |
Not exposed through this KVM path |
|
AMD KVM host with verified security fix |
Vulnerability addressed by the fix |
|
Customer VM on a shared host |
Depends on the provider's underlying host configuration |
A critical point is that a customer VM cannot reliably establish the security status of the physical host merely by checking its own kernel.
The vulnerability exists in the host virtualization layer.
Therefore, guest-level patching alone does not correct the underlying problem.
Which Kernel Versions Contain the Fix?
The Linux kernel security announcement identifies corrected releases including:
|
Kernel Branch |
Upstream Fixed Release |
|
Linux 6.12 |
6.12.118 |
|
Linux 6.18 |
6.18.64 |
|
Linux 7.3 |
7.3.5 |
The issue was also corrected in the upstream development branch.
These versions are useful reference points, but they are not a universal affected-version checklist.
Linux distributions may backport security fixes without changing to the same upstream kernel version.
For example, an enterprise distribution may continue using an older kernel version while incorporating selected security corrections.
An administrator should therefore check the distribution's security advisory and package changelog.
A version number alone may not provide enough information to determine whether a managed enterprise kernel remains vulnerable.
Why Severity Ratings Differ
Not all vulnerability assessments assign the same level of severity.
The Linux kernel CVE assessment has been reported with a CVSS score of 8.8.
Red Hat assigns a Moderate severity rating and a CVSS v3 score of 5.6.
Red Hat's public description emphasizes denial of service and memory corruption under specific conditions.
The researchers' demonstration and DigitalOcean's confirmation establish additional concerns about host memory confidentiality.
These findings should not be combined into a single unsupported severity claim.
A vendor's rating reflects its assessment of the vulnerability in the products and configurations it supports.
For operators running shared AMD virtualization infrastructure, the demonstrated guest-to-host memory access deserves particular attention.
Security Impact on Cloud Infrastructure
The primary concern is a breakdown of isolation between a guest virtual machine and its underlying host.
In shared infrastructure, that boundary separates different customers and workloads.
An attacker who can access host memory may encounter information that was never intended to be available to their VM.
The public research demonstrates that such access was possible under specific conditions.
It does not establish that every vulnerable server has been compromised.
Risk to Confidentiality
Confidentiality means preventing unauthorized access to information.
Memory belonging to a physical host can contain information used by the host operating system and running workloads.
Depending on the system's activity, sensitive information may exist in memory.
This could include application data, process information, or other runtime contents.
However, the presence of a vulnerability does not prove that a particular password, encryption key, or customer record was accessed.
The verified finding is that researchers could read a large amount of host memory.
Security teams should treat that capability as a potential exposure of sensitive information while avoiding unsupported claims about confirmed data theft.
Risk to System Integrity
Integrity concerns the accuracy and trustworthiness of system data and state.
The researchers demonstrated a controlled modification of host kernel memory on their own physical AMD server.
According to DigitalOcean, the test involved writing 32 chosen bytes into a live kernel memory page.
A separate kernel module confirmed the modification.
This result is important because the ability to alter host memory can have consequences beyond information disclosure.
Still, the published experiment should not be described as proof of persistent control over every affected host.
The demonstrated result was a specific memory modification under controlled laboratory conditions.
Availability and Service Reliability
Red Hat's advisory identifies denial of service as a potential outcome.
A denial-of-service event occurs when a system or service becomes unavailable to legitimate users.
Memory-management errors may disrupt normal execution.
In virtualization infrastructure, an affected host could potentially interrupt workloads or require recovery.
The public advisory establishes the possibility of disruption under the relevant conditions.
It does not provide evidence that widespread production outages occurred because of this CVE.
Why Small Businesses Should Care
Small businesses often depend on cloud infrastructure without directly managing the physical servers.
Their applications may run on virtual machines hosted alongside other customers.
For these organizations, the practical concern is whether the hosting provider has secured the underlying virtualization layer.
Customers using managed cloud VMs should consult their provider's security communications.
Those operating their own AMD-based KVM infrastructure have a more direct responsibility.
They must inspect the host configuration, verify the patch level, and apply the appropriate remediation.
Technical Findings and Real-World Evidence
The strongest publicly documented evidence comes from the authorized research and DigitalOcean's confirmation.
The findings are significant because they describe observed behavior rather than only a hypothetical attack.
Case Study: Host Memory Access from a DigitalOcean Droplet
The researchers began from a virtual machine under their control.
They had root privileges inside that guest environment.
This requirement matters because the demonstrated attack was not a simple unauthenticated network exploit.
The researchers used the vulnerable nested virtualization behavior to reach memory outside the guest's assigned environment.
DigitalOcean reported that the first information recovered included the host kernel's version banner.
The researchers then mapped approximately 127 GB of host RAM for reading.
The operation demonstrated that the virtualization boundary had been crossed.
DigitalOcean confirmed the finding and addressed the issue within its own infrastructure.
The provider reported deploying a live patch to its affected systems.
For Droplet customers, it stated that no customer-side action was required.
That response applies to DigitalOcean's remediation of the issue.
It should not be generalized to every cloud provider.
Separate Test: Host Kernel Memory Modification
The second demonstration took place on hardware owned by the researchers.
They used a bare-metal AMD server rather than a shared cloud host.
This distinction reduced the risk of affecting unrelated customers.
During the test, the researchers demonstrated that a guest could modify a small region of live host kernel memory.
A witness module confirmed that the selected memory content changed.
DigitalOcean reported the modification involved 32 chosen bytes.
This test supported the conclusion that the vulnerability could affect both confidentiality and integrity.
What the Evidence Does Not Establish
The public reports do not establish that attackers have broadly exploited CVE-2026-99312 against production systems.
They also do not identify a confirmed criminal campaign or named threat actor using this issue.
The research demonstrates a viable security boundary failure under controlled conditions.
That is enough to justify remediation.
It is not evidence that all AMD cloud servers have been breached.
The distinction between demonstrated capability and observed malicious activity is essential when communicating this vulnerability to customers or management.
How to Check Your Linux KVM Hosts
Administrators responsible for physical virtualization hosts should begin with configuration discovery.
The goal is to determine whether their environment meets the known exposure conditions.
These checks are defensive and do not attempt to exploit the vulnerability.
Step 1: Identify the Running Host Kernel
On the physical Linux host, run:
uname -r
The command displays the currently running kernel release.
Record the result and compare it with your distribution's security advisory.
Remember that the installed kernel package and the running kernel may differ.
A system can have an updated kernel installed while continuing to run an older version until its next reboot.
Step 2: Identify the Processor
Run:
lscpu
Review the processor vendor and virtualization information.
For the vulnerability discussed here, AMD-based KVM hosts require particular attention.
The processor type alone does not establish that the vulnerability is exploitable.
Nested virtualization and the applicable kernel code must also be considered.
Step 3: Check Nested Virtualization
On an AMD KVM host, inspect the relevant module parameter:
cat /sys/module/kvm_amd/parameters/nested
A value indicating that nested virtualization is enabled means the feature is available in the running host configuration.
A value indicating that it is disabled suggests the documented attack path is unavailable.
The parameter file may not exist if the relevant module is not loaded or the system uses a different configuration.
Administrators should interpret the result alongside their virtualization setup.
Step 4: Verify Installed Security Updates
Use the package-management tools appropriate for the host operating system.
For Debian-based systems:
apt list --upgradable
For RPM-based environments using DNF:
dnf check-update
These commands help identify available package updates.
They do not independently prove that CVE-2026-99312 is fixed.
The next step is to review the distribution's official security notices and package changelogs.
Where available, confirm the presence of the relevant backported kernel correction.
Step 5: Check the Active Kernel After Maintenance
Following an approved kernel update and required reboot, run:
uname -r
Confirm that the expected kernel is active.
Then check the host's vendor advisory again to ensure the installed release includes the correction.
For production virtualization clusters, this verification should be included in the maintenance record.
A successful package installation is not the same as confirming the fix is running.
How to Mitigate CVE-2026-99312
The main remediation is to install a Linux kernel version containing the relevant KVM correction.
For hosts that cannot be patched immediately, disabling nested virtualization may reduce exposure to the documented attack path.
These actions should be planned carefully because changes to virtualization settings can affect running workloads.
Priority 1: Apply the Vendor-Supported Kernel Fix
Administrators should identify the distribution and kernel branch used by each AMD KVM host.
Next, consult the operating system vendor's advisory for CVE-2026-99312.
Install the approved kernel update according to the vendor's instructions.
A controlled reboot may be necessary to activate the new kernel.
Before rebooting a production host, review the workloads assigned to it.
Where supported, migrate running VMs to appropriately secured hosts.
After maintenance, verify the active kernel and service health.
This process reduces the chance that a security update itself causes avoidable service disruption.
Priority 2: Disable Unnecessary Nested Virtualization
Nested virtualization should remain enabled only when required by legitimate workloads.
The Linux kernel supports configuration of the AMD KVM nested virtualization feature through its module parameters.
For a planned configuration change, the documented kernel command-line parameter is:
kvm_amd.nested=0
This setting disables AMD KVM nested virtualization when applied correctly.
The procedure for making the change persistent depends on the distribution and boot configuration.
Administrators should follow their vendor's documented process.
Do not unload active virtualization modules or interrupt production workloads simply to change the setting.
Disabling nested virtualization can prevent nested VMs from operating.
Therefore, identify affected workloads and schedule the change before applying it.
Priority 3: Review Shared-Host Exposure
Organizations operating multiple virtual machines on the same physical host should identify which systems share the affected hardware.
Record the host's processor, kernel version, nested virtualization status, and patch status.
Prioritize hosts that support untrusted or externally controlled guest workloads.
This is a risk-based recommendation, not a claim that such hosts have already been compromised.
The objective is to address environments where a guest-to-host boundary failure would have the greatest business impact.
Priority 4: Confirm Cloud Provider Remediation
Organizations renting virtual machines usually do not control the provider's physical host kernel.
They should request or review the provider's official security information.
Useful questions include whether the infrastructure uses affected AMD KVM configurations and whether the host-side correction has been deployed.
DigitalOcean publicly confirmed its remediation.
That statement cannot establish the status of unrelated providers.
A customer should not assume that updating the operating system inside a rented virtual machine fixes the provider's hypervisor.
Mitigation Priority Table
|
Action |
Purpose |
Priority |
|
Install verified host kernel correction |
Remove the underlying vulnerability |
High |
|
Disable nested virtualization if unused |
Remove the documented exposure condition |
High |
|
Verify running kernel after maintenance |
Confirm the correction is active |
High |
|
Review shared-host configurations |
Identify potentially exposed environments |
High |
|
Consult cloud provider advisories |
Establish provider-specific remediation status |
High |
|
Maintain change and patch records |
Support verification and future review |
Ongoing |

Detection and Incident Response
A difficult aspect of CVE-2026-99312 is that the public evidence does not establish a reliable set of attack indicators for defenders.
Traditional monitoring tools may record guest activity, host errors, or unexpected system behavior.
However, those events are not necessarily unique to this vulnerability.
At the time of the reviewed disclosures, no confirmed general-purpose detection signature had been established in the cited primary sources.
Security teams should therefore avoid presenting ordinary virtualization warnings as proof of exploitation.
What Administrators Can Investigate
Organizations investigating a potentially affected host can begin by reviewing its configuration and patch history.
Determine whether nested virtualization was enabled during the relevant period.
Identify which guest VMs had access to that functionality.
Review available virtualization logs and existing security-monitoring records.
Preserve relevant evidence before making disruptive changes where a security incident is suspected.
These actions can support an investigation.
They cannot guarantee that a past exploitation attempt will be identified.
Distinguishing Exposure from Compromise
Exposure means a system contains the conditions required for a vulnerability to be relevant.
Compromise means an attacker has successfully used an attack path to violate a security boundary.
A vulnerable AMD KVM host is not automatically a compromised host.
Likewise, a system crash does not prove that this particular CVE was exploited.
An incident report should clearly separate confirmed evidence from possible explanations.
If unauthorized access is suspected, organizations should follow their established incident-response procedures and obtain qualified forensic assistance.
Practical Response for CISOs
For security leaders, the first question is not whether every system runs Linux.
It is whether the organization operates or depends on affected AMD nested virtualization infrastructure.
The next question concerns control.
Can the organization patch the physical host directly, or must it rely on a cloud provider?
The answer determines who is responsible for remediation and what evidence should be requested.
Security leaders should also assess the business importance of workloads hosted on potentially affected servers.
Systems processing sensitive customer data may require closer review.
However, the existence of sensitive workloads does not establish that their contents were exposed.
The response should remain proportionate to verified technical conditions.
Why a Previous Security Fix Matters
One notable aspect of the research is the reported connection to an earlier KVM security correction.
The investigators linked the underlying problem to changes associated with CVE-2022-3344.
According to their analysis, the earlier correction changed how the virtualization system handled part of a nested reset operation.
The memory-management pointer was not fully restored in the affected path.
This created the conditions for the later vulnerability.
The important lesson is not that security patches should be avoided.
It is that changes to low-level virtualization code require careful testing of related processor and memory states.
A correction may resolve one problem while leaving an unexpected interaction elsewhere.
Security Testing Beyond the Original Bug
Virtualization code manages complicated transitions between processor states.
Changes affecting reset behavior, memory mapping, or nested execution deserve particular attention.
A useful review should consider not only whether the original defect is fixed but also whether related state transitions remain consistent.
For example, a reset operation may behave differently depending on whether paging is enabled.
Testing both conditions can help identify unexpected differences.
This is a general engineering observation supported by the nature of the documented failure.
It is not a claim that any particular vendor failed to follow a specific testing procedure.
What This Means for the Future of Virtualization Security
CVE-2026-99312 illustrates how a small error in memory-management state can have consequences beyond the affected function.
The vulnerability was not a conventional application bug.
It involved the software layer responsible for keeping virtual machines separate.
When that layer fails to maintain correct memory mappings, the impact can extend beyond one guest operating system.
The findings also show why researchers, infrastructure providers, and upstream maintainers need coordinated disclosure processes.
The Linux kernel correction was merged before the public announcement.
DigitalOcean also confirmed its response before publishing its detailed statement.
Those actions helped provide administrators with a documented remediation path when the vulnerability became public.
The larger operational lesson is straightforward.
Virtualization security depends on more than guest operating system updates.
Physical host configuration, kernel maintenance, and access to nested virtualization must also be managed.
For organizations operating shared infrastructure, these controls are central to maintaining reliable isolation.
Frequently Asked Questions
1. What is CVE-2026-99312 in Linux KVM?
CVE-2026-99312 is a Linux KVM vulnerability involving incorrect memory-management state during INIT reset emulation.
It affects specific AMD-based nested virtualization configurations.
Researchers demonstrated that the flaw could allow a guest virtual machine to access memory belonging to its physical host.
2. Does CVE-2026-99312 Affect All Linux Servers?
No.
The documented guest-to-host memory exposure depends on specific virtualization conditions.
AMD KVM hosts with affected code and nested virtualization enabled are the primary concern.
Linux servers that do not use the relevant functionality are not exposed through this particular attack path.
Administrators should consult their operating system vendor's advisory to confirm applicability.
3. How Can Administrators Fix CVE-2026-99312?
The primary fix is to update the physical host's Linux kernel to a version containing the correction.
Upstream fixed releases include Linux 6.12.118, 6.18.64, and 7.3.5.
Distribution-specific backports may provide the correction in other kernel versions.
Disabling unnecessary AMD nested virtualization is an additional defensive measure when immediate patching is not possible.
4. Has CVE-2026-99312 Been Exploited in Real Attacks?
The cited public reporting confirms exploitation during authorized security research.
It does not establish a widespread malicious exploitation campaign.
The researchers demonstrated host memory access in a cloud environment and memory modification in a separate controlled test.
Organizations should address the vulnerability without describing unverified criminal activity as confirmed.
Final Thoughts
The Linux KVM vulnerability CVE-2026-99312 highlights a serious risk in affected AMD nested virtualization environments.
Researchers demonstrated access to approximately 127 GB of host memory from a guest virtual machine. A separate controlled experiment showed that modification of host kernel memory was also possible.
These findings illustrate the importance of enforcing virtualization boundaries correctly.
They do not establish that all AMD servers are vulnerable or that widespread data theft has occurred.
For administrators, the next step is to verify the underlying host configuration and patch status.
For cloud customers, it is to obtain reliable information from the infrastructure provider.
The most important lesson is that a virtual machine's security depends partly on the physical systems beneath it.
Keeping those systems patched and limiting unnecessary virtualization features remain essential defensive responsibilities.
Author Bio and Review
Author: Sharfun Nahar Radia is a cybersecurity writer and analyst with over five years of experience covering emerging threats, vulnerabilities, and digital security trends. She holds professional certifications in cybersecurity, strengthening her expertise in security research and analysis.
Technical reviewer: Gazi Mahmud, Co-Founder
and CIO of Hoplon InfoSec LLC, cybersecurity leader, and CISM & CISA
certified professional with expertise in cyber risk management, security
governance, compliance, and incident response.
Sources and Verification
The technical claims in this article are based on the following publicly available sources:
1. Linux Kernel CVE Announcement
CVE-2026-99312: KVM: x86: Unconditionally reset MMU context when emulating INIT
2. Official CVE Record
3. Red Hat Security Advisory
Read More Articles:
Genea IVF Cyberattack and Patient Data Security Risks
Dangers of Deepfake Technology
Cybersecurity Weekly Recap: Threats and Attacks
Marks & Spencer Cybersecurity Breach
CVE-2024-24919 Check Point VPN Zero-Day Vulnerability
CISA Releases 10 New ICS Security Advisories
Best Practices for Cloud Security
Apache Tomcat Security Vulnerability