If you searched “gmail hacked” after seeing reports about millions of exposed accounts, there is an important distinction to understand first:
Google said Gmail itself was not breached in the October 2025 incident that generated the “183 million Gmail accounts hacked” headlines.
The 183 million figure came from a large collection of stolen credentials gathered from infostealer activity across the internet. It was not evidence that attackers broke into Gmail’s infrastructure and stole 183 million Gmail passwords directly from Google.
That does not mean every Gmail user is automatically safe.
If your password was stolen elsewhere, captured by malware, reused across websites, phished from you, or exposed through another breach, an attacker may still be able to compromise your Google Account.
So there are really two different questions:
- Was Gmail itself hacked in a new 183-million-account breach? Google says no.
- Could your individual Gmail account still be compromised? Yes.
This guide explains both.
Key Findings
|
Question |
What the evidence shows |
|
Were 183 million Gmail accounts breached directly from Google? |
No evidence supports that claim. Google denied a new mass Gmail breach. |
|
What did the 183M figure represent? |
About 183 million unique email addresses in Synthient stealer-log data collected from credential theft activity across the web. |
|
Was all of the data new? |
No. Troy Hunt reported that most addresses had already appeared in HIBP datasets, although millions were previously unseen there. |
|
Can old leaked passwords still compromise Gmail? |
Yes, particularly when passwords are reused or stolen credentials remain valid. |
|
Should you change your password just because of the headline? |
Not necessarily. But change it immediately if it is reused, exposed, weak, or you see suspicious activity. |
|
Is 2FA enough by itself? |
It is an important protection, but session-cookie theft and some advanced attacks can still create risk. |
|
What should a compromised user check beyond the password? |
Recovery information, devices, security events, connected apps, Gmail forwarding, filters, delegation, POP/IMAP and other altered settings. |
The distinction between a platform breach and stolen user credentials is the most important part of this story.
What Actually Happened With the “183 Million Gmail Accounts” Story?
In October 2025, reports began circulating that roughly 183 million Gmail passwords or accounts had been exposed.
That description was misleading.
Have I Been Pwned creator Troy Hunt documented a large dataset supplied by threat-intelligence project Synthient. The stealer-log portion contained about 183 million unique email addresses.
Stealer logs generally come from information-stealing malware running on compromised devices. That malware can capture combinations such as:
- Website address
- Email address or username
- Password
If someone signs into Google while an infected machine is recording credentials, a Gmail or Google login can appear in that collection even though Google's own servers were never breached.
Have I Been Pwned continues to list the Synthient Stealer Log Threat Data as a dataset containing approximately 183 million accounts.
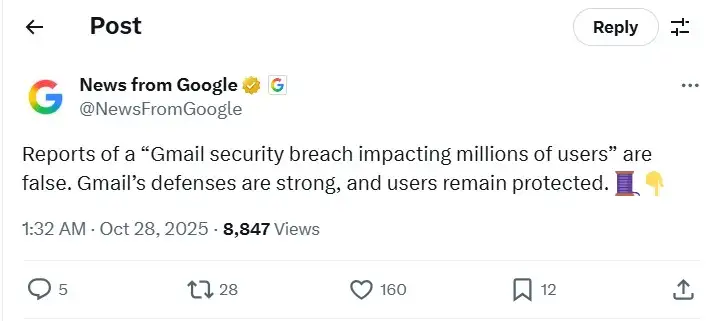
Google denied a new Gmail breach
On October 27, 2025, Google publicly rejected reports that millions of Gmail users had been affected by a new Gmail security breach.
Google explained that the reports resulted from a misunderstanding of infostealer databases, which aggregate credentials stolen through many incidents across the web rather than representing one attack against Gmail.
You can view Google's original statement on X.
So where did the credentials come from?
Potential sources include:
- Information-stealing malware
- Phishing pages
- Previously compromised websites
- Credential collections
- Reused passwords
- Credential-stuffing operations
An infostealer does not need to compromise Google's infrastructure. It attacks the user's device or browser environment instead.
For a practical example of how this category of malware steals credentials, Hoplon Infosec's analysis of infostealer malware hidden in a fake software repository explains how credentials can be taken before the legitimate service itself is ever breached.
Why Did “Gmail Hacked” Sound So Much Worse?
Large credential collections are easy to misinterpret.
Suppose researchers discover millions of records containing email addresses and passwords. Some addresses end in Gmail or are associated with Google logins.
A headline might shorten that into:
“Millions of Gmail passwords leaked.”
That sounds like Google was hacked.
But those are different security events.
A genuine Gmail infrastructure breach would mean attackers compromised systems operated by Google and extracted data from them.
A credential collection may instead contain passwords stolen individually from infected computers, phishing victims, old breaches and other unrelated sources.
This distinction matters because the response is different.
Google's Gmail protections themselves remain substantial. Google states that Gmail blocks more than 99.9% of spam, phishing attempts and malware before they reach users. That statistic describes Gmail's filtering capabilities, not a guarantee that individual accounts can never be compromised.
What Does “Gmail Hacked Password Changed” Actually Mean?
If your Gmail password changed without your permission, treat that as a possible account takeover regardless of whether Google suffered a wider breach.
There are several realistic ways it could happen.
1. You reused a password
Imagine that you used the same password for Gmail and another website.
That website was breached two years ago.
An attacker later obtains the email-password combination and tests it against Google.
If the password still works, your Gmail account may be compromised even though Gmail itself was never breached.
This type of attack is known as credential stuffing.
You can read Hoplon Infosec's explanation of how credential stuffing attacks use stolen login combinations.
2. Your password was captured by infostealer malware
Malware running on a computer can capture passwords entered into websites or collect browser data.
Changing the Gmail password is important, but if the infected device remains compromised, the attacker may simply steal new information again.
3. You entered credentials into a phishing page
A fake Google security alert may claim:
- Your Gmail was hacked
- Your password expired
- Someone accessed your account
- Verify your identity immediately
- Your mailbox will be suspended
The attacker wants the panic surrounding a security incident to push you into clicking before checking the message.
Hoplon Infosec's guide to common phishing attack types and fake login scams explains how these attacks work.
If you already interacted with a suspicious page, use this response guide for what to do after you have clicked a phishing link.
4. Your existing authenticated session was stolen
This point is especially important for people searching “Gmail hacked with 2FA.”
Two-step verification greatly improves account security, but it is not a guarantee against every attack.
Google Cloud has specifically discussed infostealers that exfiltrate authenticated session cookies. A stolen valid session can sometimes allow attackers to bypass the normal password and 2FA login process.
That is why an account compromise response should include more than simply changing your password.
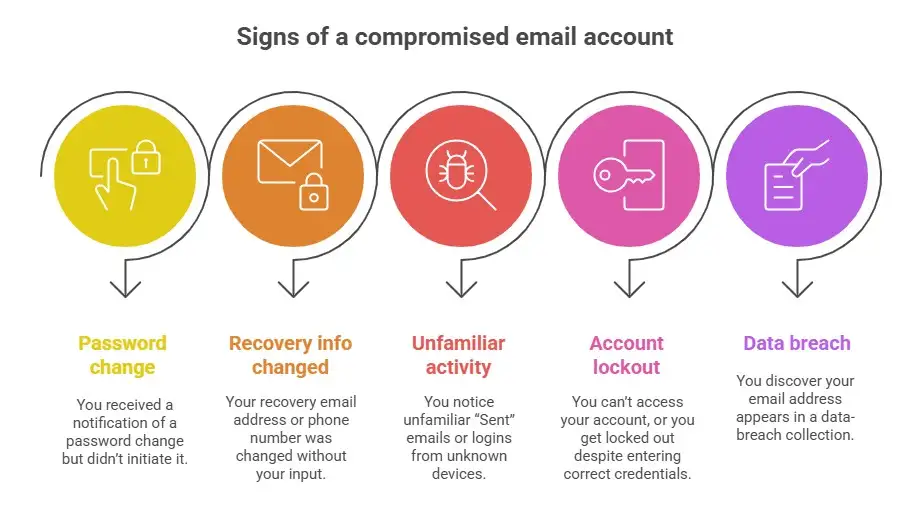
How to Tell If Your Gmail Was Hacked
Google identifies several signs that may indicate someone else is using your account.
Pay particular attention to the following.
Your password changed without your permission
If Google tells you your password was changed and you did not make the change, begin recovery immediately.
Your recovery email or phone number changed
Unauthorized changes to recovery information are particularly serious because attackers may be trying to make it harder for you to regain control.
You see unfamiliar devices
Check the devices connected to your Google Account.
A device, browser or location you cannot explain deserves investigation.
You find unfamiliar security events
Google's Recent Security Activity can show suspicious sign-ins and account-setting changes.
Emails appear in Sent that you did not write
Attackers sometimes use compromised Gmail accounts for:
- Spam
- Phishing
- Fraud
- Password resets
- Impersonation
Friends receive strange emails from you
This may indicate that someone has used your real account to send malicious or fraudulent messages.
Emails disappear
Unexpected deletion or disappearance of messages can indicate that Gmail settings were altered.
You stop receiving important emails
An attacker may create filters or forwarding rules that redirect or delete security notifications, invoices, password-reset messages or business communications.
Your account is suddenly inaccessible
If your known password no longer works and account information has been changed, the account may have been hijacked.
Your email appears in a breach database
You can check your address using Have I Been Pwned.
Finding your email there does not automatically mean Gmail itself was hacked. It means the address appeared in a breach or credential dataset tracked by the service.
Gmail Hacked Password Changed and Recovery Email Changed: What to Do
If both your password and recovery information were changed, act quickly.
Google's official account-recovery process is the main route for recovering a personal Google Account.
Use the official Google Account Recovery page.
Avoid websites, social-media accounts or individuals claiming they can “manually unlock” a Gmail account in exchange for money or passwords.
Google's current guidance specifically warns against account or password recovery services and states that users should not give anyone their passwords or verification codes.
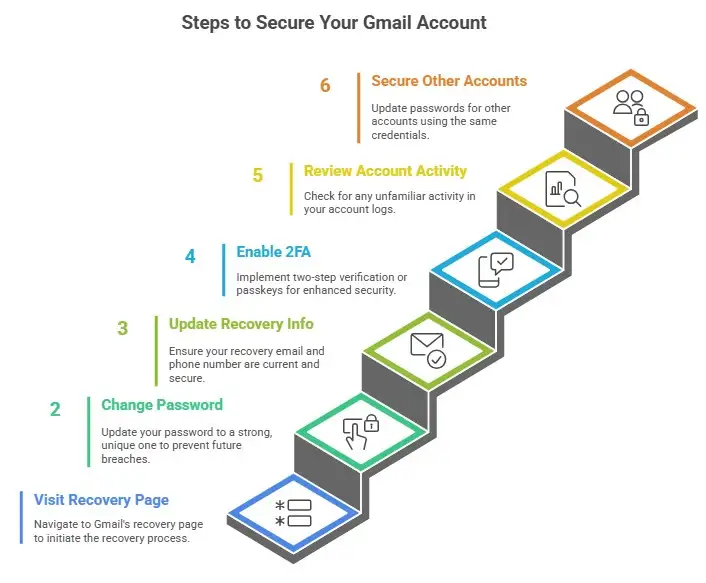
Path A: You Can Still Access the Gmail Account
If you still have access from a phone, browser or computer, secure the account before the attacker can lock you out.
Step 1: Change the Google Account password
Use a password that is:
- Unique to Google
- Not used on another website
- Long
- Difficult to guess
- Stored securely
Hoplon Infosec's guide on how to create a strong password explains the practical approach to long, unique passwords and password managers.
Do not simply add one character to the old compromised password.
Step 2: Review your recovery email and phone
Make sure every recovery method belongs to you.
Remove information you do not recognize.
Google says recovery information may also help alert users to suspicious activity and restore access when they are locked out.
Step 3: Review Recent Security Activity
Look for:
- Unknown logins
- New devices
- Recovery changes
- 2-Step Verification changes
- New authentication methods
- Suspicious app access
Mark unfamiliar activity as unauthorized when Google provides that option.
Step 4: Review connected devices
Remove or sign out devices you do not recognize.
Do not assume changing the password alone has completed the cleanup.
Step 5: Review third-party access
Check apps and services connected to the Google Account.
Remove anything:
- You do not recognize
- You no longer use
- You did not authorize
Step 6: Check Gmail's hidden persistence settings
This is one of the most commonly missed steps after a Gmail compromise.
Google specifically recommends checking Gmail for unauthorized settings such as forwarding rules, filters and delegation.
Review:
Forwarding and POP/IMAP
- Is mail being forwarded to another address?
- Are POP or IMAP settings unfamiliar?
Filters and Blocked Addresses
- Is a filter forwarding messages?
- Is a filter automatically deleting messages?
- Is a filter skipping the inbox?
Accounts and Import
- Is an unknown address listed under “Send mail as”?
- Has someone been granted access to your account?
- Is Gmail checking mail from an unfamiliar account?
General Settings
- Has your signature changed?
- Is an unexpected vacation responder active?
Attackers may use these settings to maintain visibility into your email even after you reset the password.
Step 7: Check the device for malware
If an infostealer caused the original compromise, changing passwords from the infected computer may expose the new password too.
Update your operating system and security tools, remove suspicious software and extensions, and run a trusted malware scan.
Path B: You Are Completely Locked Out
If the attacker changed the password or recovery information and you can no longer sign in, use Google's recovery process.
Answer Google's questions as accurately as you can.
Helpful practices include:
- Use a device you previously used with that account
- Use a familiar browser
- Try from a familiar location or network
- Provide a previous password when requested
- Use recovery methods still available to you
- Do not intentionally guess information you know is false
Google's current documentation does not promise that every user will receive the same recovery questions. The prompts can vary.
Some older recovery articles mention details such as account creation dates. Treat the current Google recovery flow as authoritative and provide whatever historical information it actually requests.
Google also notes that changes to recovery information or authentication factors can involve security waiting periods. In some situations, previous recovery information may remain useful temporarily after a change.
After Recovering Gmail, Secure Every Reused Password
Recovering Gmail is only part of the incident response.
If the Gmail password was also used on:
- Banking services
- Shopping sites
- Cloud platforms
- Business dashboards
- Hosting accounts
- Cryptocurrency services
- Microsoft accounts
- Other email services
change those passwords too.
Do not replace them all with another shared password.
A password manager allows each service to have its own unique credential.
This breaks the chain that makes credential stuffing effective.
Enable 2-Step Verification
Two-step verification adds another authentication requirement beyond the password.
Google says 2-Step Verification can protect an account even when the password itself has been stolen.
Hoplon Infosec's comparison of 2FA vs MFA and stronger authentication options explains the difference between these approaches.
Google supports multiple verification methods, including:
- Google prompts
- Authenticator applications
- Security keys
- Passkeys
- Verification codes
Security keys and passkeys provide stronger phishing resistance than traditional password-only authentication.
Consider Using a Passkey
Google describes passkeys as a more secure alternative to passwords.
Instead of typing a reusable secret into a website, you authenticate using a device you control, such as through:
- Fingerprint
- Face recognition
- Device PIN
- Hardware security key
Google says passkeys are resistant to phishing because the credential cannot simply be typed into and stolen by a fake login page.
This makes passkeys particularly useful for accounts that protect sensitive business or personal information.
Can Gmail Still Be Hacked With 2FA Enabled?
Yes, account compromise is still possible, although 2FA substantially reduces many password-based risks.
Common possibilities include:
MFA phishing
An attacker may try to trick you into approving a legitimate authentication request.
Social engineering
A criminal may impersonate Google, your employer, an administrator or another trusted person.
Malware
A compromised endpoint can steal information directly from the device.
Session-cookie theft
This is especially important.
Google Cloud has described infostealers capable of stealing session cookies that may allow attackers to bypass the normal password and 2FA process.
This is why endpoint security, session management and device hygiene matter alongside 2FA.
How to Protect Gmail Against Future Attacks
A secure Gmail account requires several layers of protection.
1. Never reuse your Gmail password
A unique password prevents a breach on one unrelated website from automatically exposing your Gmail account.
2. Use a password manager
Password managers make it practical to maintain separate, complex passwords across many accounts.
3. Enable 2-Step Verification
Do not rely on your password alone.
4. Prefer phishing-resistant authentication
Where practical, use passkeys or security keys.
5. Keep recovery information updated
Your recovery phone and email may become critical if you lose access.
6. Review account activity periodically
Check devices and security events before suspicious activity becomes a larger problem.
7. Learn to identify phishing
Security alerts themselves can be used as phishing bait.
Do not click a link solely because an email claims:
“Your Gmail has been hacked.”
Instead, open Google through the normal website or app and check the account directly.
8. Keep your device clean
A perfectly configured Gmail account cannot fully protect credentials being stolen directly from an infected computer.
Keep:
- Operating systems updated
- Browsers updated
- Security software current
- Browser extensions limited to trusted tools
- Unknown software off sensitive devices
9. Protect business email as a system
For organizations, Gmail or Google Workspace security should not depend entirely on individual employee decisions.
Email security should include account protection, phishing controls, employee awareness, authentication, endpoint monitoring and incident response.
Hoplon Infosec's email security best-practices guide covers this broader defensive approach.
Why the Gmail Breach Story Matters to Businesses
Email is often the control center for the rest of a person's digital identity.
Access to one email account may help an attacker reset passwords for:
- Social media
- Business applications
- Financial platforms
- Cloud accounts
- Customer systems
- E-commerce services
- Collaboration platforms
For a business owner or administrator, a compromised mailbox can also expose confidential conversations, password-reset links, invoices and internal contacts.
That is why the correct response to the October 2025 Gmail story is not panic.
It is understanding the actual threat.
Google said there was no new mass Gmail infrastructure breach. But credential theft, password reuse, phishing, malware and session hijacking remain real account-level risks.
What If Your Email Appears in Have I Been Pwned?
Do not assume the worst.
An HIBP result means the email address appeared in data that the service has indexed.
Ask three questions:
Was a password exposed?
If yes, change any account still using that password.
Is that password reused?
If yes, replace it everywhere it is still active.
Is there evidence of actual Gmail account activity?
Check Google's security events, devices and Gmail settings.
An email appearing in a breach database is evidence of exposure, not proof that an attacker currently controls your Gmail account.
What About “Gmail Hacked Website” Searches?
The phrase can describe several different situations.
A website where you used your Gmail address may have been breached.
A phishing website may have stolen your Google password.
Malware may have recorded your Gmail login.
Or your Google Account itself may have been taken over.
These situations should not all be described as “Gmail was hacked.”
The source of the credential theft matters.
When Should a Business Involve Its IT or Security Team?
Report the incident immediately if the account is connected to:
- Company systems
- Google Workspace
- Customer information
- Financial accounts
- Administrator privileges
- Sensitive files
- Cloud infrastructure
- Password managers
- Internal communication systems
The security team may need to investigate more than the mailbox itself.
Possible areas include:
- Endpoint compromise
- Session theft
- OAuth or third-party application access
- Phishing
- Lateral movement
- Password reuse
- Other affected identities
For organizations that need stronger protection against phishing and mailbox compromise, Hoplon Infosec also provides email security and anti-phishing services.
Professional assistance should complement Google's account-recovery process, not replace or bypass Google's ownership verification.
Frequently Asked Questions
How can I tell if my Gmail was hacked?
Look for unauthorized password changes, altered recovery information, unfamiliar devices, unexpected security events, emails you did not send, missing messages or account settings you did not configure.
Google recommends reviewing Recent Security Activity, connected devices and Gmail security settings.
My Gmail password and recovery email were changed. What should I do?
Start Google's official account-recovery process immediately.
If you regain access:
- Change the password.
- Restore recovery information.
- Remove unfamiliar devices.
- Review connected apps.
- Check Gmail forwarding, filters and delegation.
- Enable 2-Step Verification.
- Check your device for malware.
I heard that a “Gmail hacked website” exposed passwords. Was Gmail itself hacked?
Not necessarily.
The October 2025 story involving approximately 183 million email addresses did not establish a new breach of Gmail's infrastructure.
Google specifically rejected that interpretation. The dataset came from wider credential-theft activity.
Can Gmail be hacked even if I use 2FA?
2FA substantially improves account security, but no single security control stops every possible attack.
Phishing, malware, social engineering and stolen authenticated sessions can create additional risks.
Google Cloud has specifically discussed session-cookie theft by infostealers as a way attackers can bypass password and 2FA controls.
Where should I report a hacked Gmail account?
For a personal Google Account, begin with Google's official account recovery and compromised-account guidance.
If the Gmail account belongs to an organization, contact the organization's administrator or IT/security team immediately.
If the compromise leads to financial fraud, identity theft or other criminal activity, additional reporting to the relevant financial institution or authorities may also be appropriate.
Should I change my password even if Google says Gmail was not breached?
Change it if:
- It appears to have been exposed
- You reuse it on another service
- Someone logged into your account
- You entered it into a phishing page
- Malware may have stolen it
- It is weak or predictable
If you already use a unique, uncompromised password and have no evidence of suspicious activity, the October 2025 headline alone does not prove that the password needs emergency replacement.
Final Takeaway
The headline “183 million Gmail accounts hacked” did not accurately describe what happened.
Google said there was no new mass breach of Gmail itself. The underlying dataset contained credentials gathered through wider infostealer and credential-theft activity across the web.
But that distinction should not lead to complacency.
A Gmail account can still be compromised through:
- Password reuse
- Phishing
- Infostealer malware
- Credential stuffing
- Social engineering
- Stolen sessions
- Weak recovery security
If your password changed unexpectedly, your recovery email was replaced, or unfamiliar activity appears in the account, treat the situation as an actual account-security incident.
Recover the account through Google, secure every authentication and recovery method, inspect Gmail's forwarding and filter settings, clean potentially infected devices, and replace any passwords that were reused elsewhere.
The goal is not to react to every frightening headline.
It is to know the difference between a platform breach and an individual account compromise, then respond to the evidence you actually have.
You can also read these important cyber security news articles on our website.
· Apple Update,