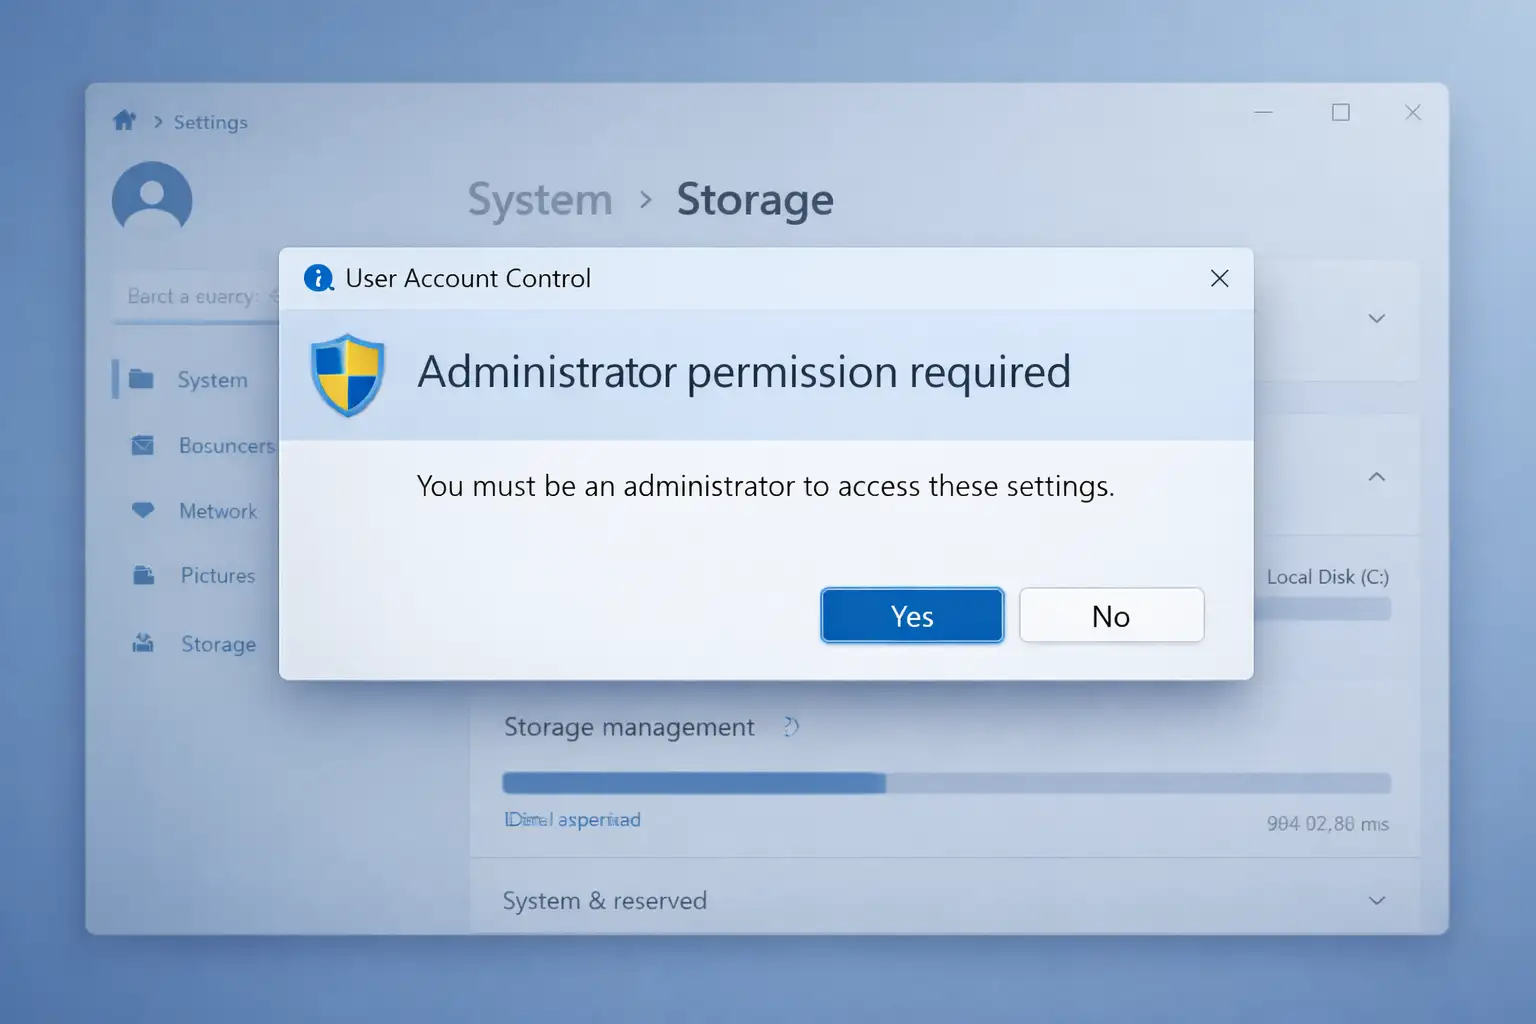
Windows 11 KB5074105 introduced a new admin access requirement for Storage settings. After installing the January 2026 preview update, users may now see a User Account Control (UAC) prompt when opening Settings > System > Storage.
Microsoft says the change is intended to help ensure that only authorized Windows users can access system files. This article explains what the KB5074105 Storage admin access change does, why it matters, who is affected, and how to deal with it.
What is Windows 11 KB5074105?
KB5074105 is a non-security preview update released on January 29, 2026 for Windows 11 version 24H2 and 25H2. While the update includes general fixes and reliability improvements, one of the most discussed changes is a new admin access prompt for the Storage settings page.
This is the change most users are referring to when they search for “Windows 11 KB5074105 storage admin access.
September 2026 Verification: What Microsoft Still Documents
As of September 1, 2026, Microsoft’s live KB5074105 support page still documents the Storage settings elevation behavior. The official changelog states that Windows displays a User Account Control (UAC) prompt when users open Settings > System > Storage so that access to system files is limited to authorized Windows users. Microsoft also continues to list the same Storage change in the update’s quality-improvement notes.
This matters because several other features that were originally listed for KB5074105 were later removed from Microsoft’s documentation and planned for future releases. The Storage UAC requirement was not removed in those change-log entries and remains documented on the current support page.
Microsoft’s page also says it is not currently aware of any known issues with KB5074105. That official status should be distinguished from user reports and third-party testing about Storage and Temporary files behavior, which are discussed later in this guide.
For readers comparing preview releases with later monthly packages, Hoplon Infosec’s guide to Windows 11 cumulative updates explains how Microsoft combines fixes, security changes, and reliability improvements across Windows update cycles.
KB5074105 Build Numbers and Release Details
KB5074105 was released on January 29, 2026 as an optional non-security preview update for Windows 11 versions 24H2 and 25H2. The update corresponds to OS Build 26100.7705 for Windows 11 24H2 and OS Build 26200.7705 for Windows 11 25H2.
Because this was a preview update rather than a Patch Tuesday security release, it was designed to deliver upcoming fixes and features ahead of the next regular servicing cycle. That distinction is useful when troubleshooting because a preview build can introduce behavior that users did not see on the previous production build.
Quick Summary: What Changed in KB5074105?
Many users searching for the Windows 11 KB5074105 storage admin access change want a quick answer before reading technical details.
At a Glance
|
Feature |
Before KB5074105 |
After KB5074105 |
|
Storage Settings Access |
Open to all users |
Requires UAC approval |
|
System Storage Visibility |
Standard users could view details |
Restricted |
|
Administrative Approval |
Not required |
Required |
|
Security Protection |
Standard |
Enhanced |
This update introduces an additional security checkpoint before Windows displays sensitive storage-related system information.
Why Microsoft Introduced This Security Change
Microsoft's decision reflects a broader shift toward Zero Trust security principles.
Rather than assuming users inside a system are trustworthy, modern operating systems increasingly verify access requests before exposing sensitive information.
Security Goals Behind the Change
Reduce unauthorized system exploration
Strengthen least-privilege access controls
Limit information gathering by malware
Protect shared and managed devices
Improve enterprise security compliance
This aligns with Microsoft's long-term security roadmap across Windows 11.
How KB5074105 Supports Zero Trust Security
Zero Trust has become one of Microsoft's most important security strategies.
The core principle is simple: never trust, always verify.
Under this model, even authenticated users may need additional approval before accessing sensitive resources.
How This Relates to Storage Settings
The Storage page can reveal:
System-reserved partitions
Operating system files
Update cache information
Recovery data
Temporary system resources
Microsoft now treats access to this information as a privileged action rather than a standard user task.
What the UAC Prompt Actually Changes in the Security Model
The Storage prompt is best understood as an elevation boundary, not as a replacement for Windows file permissions. UAC checks whether an action needs an administrator-level access token and asks an administrator to approve or provide credentials when elevation is required. Existing NTFS permissions and other Windows access controls still apply after that elevation step.
That distinction is important for security teams. A UAC prompt can reduce what a process running with ordinary user rights can do, but it does not make the device immune to malware, privilege-escalation vulnerabilities, or misuse by an already elevated administrator. This is why the change fits more naturally into a layered endpoint security strategy rather than being treated as a complete protection by itself.
Potential Enterprise Benefits
Organizations may see significant security advantages from the new access restrictions.
Business Benefits
Reduced insider threat visibility
Better least-privilege enforcement
Stronger endpoint security posture
Improved audit readiness
Better protection of shared workstations
For organizations pursuing compliance frameworks, this change may help strengthen security controls around system visibility.
Compatibility Considerations for IT Teams
Before broad deployment, administrators should evaluate how the change affects internal workflows.
Areas to Test
Monitoring tools
Inventory software
Endpoint management platforms
PowerShell automation
Custom administrative scripts
Storage reporting tools
Some tools may require elevated permissions after the update.
Add KB5074105 to Patch and Exposure Validation
For managed environments, testing should include more than confirming that the Storage page opens. IT teams should verify whether endpoint inventory tools, help-desk procedures, remote support workflows, scripts, and cleanup routines behave differently when the Storage interface requires elevation.
Organizations that already use a formal vulnerability management process can treat this as a configuration and operational validation task: identify affected Windows 11 builds, test representative endpoints, document any workflow change, and confirm that the final configuration still follows least-privilege requirements.
Known Limitations of the New Security Feature
While the feature improves security, it may introduce some usability challenges.
Potential Limitations
|
Limitation |
Impact |
|
Additional UAC prompts |
More user interaction |
|
Standard user restrictions |
Reduced visibility |
|
Script compatibility issues |
Enterprise testing required |
|
Shared PC workflow changes |
Additional admin approvals |
Most organizations will likely view these trade-offs as acceptable given the security benefits.
Security Comparison: Before vs After KB5074105
The update represents a significant change in how Windows protects system-level information.
|
Security Area |
Before Update |
After Update |
|
Storage Visibility |
Broad Access |
Restricted Access |
|
UAC Enforcement |
Limited |
Expanded |
|
Administrative Control |
Moderate |
Stronger |
|
System Information Exposure |
Higher |
Lower |
|
Enterprise Security |
Standard |
Enhanced |
Future Windows Security Changes to Expect
KB5074105 is unlikely to be the last change of this kind.
Microsoft has increasingly moved toward protecting sensitive operating system components through layered security controls.
Future Windows releases may introduce similar protections for:
Device Manager
Advanced Network Settings
Recovery Configuration
Security Configuration Areas
System Diagnostic Tools
Organizations should expect additional privilege-based access controls in future Windows 11 updates.
Why This Change Matters Alongside Other Windows Hardening Updates
KB5074105 is part of a wider pattern in which Microsoft is tightening access to sensitive Windows components and privileged operations. Other Windows security work has focused on areas such as Secure Boot, application control, authentication, driver trust, and privilege boundaries.
Readers following that broader direction can compare this Storage elevation change with Hoplon Infosec’s coverage of Windows 11 driver security changes and the Windows 11 March 2026 update. These updates are not the same feature as KB5074105, but they provide useful context for Microsoft’s continuing Windows 11 hardening work.
Administrator Deployment Checklist
Before deploying KB5074105 across production devices, IT teams should complete the following checks.
Pre-Deployment Checklist
- Verify administrator account access
- Test on pilot devices
- Review Group Policy settings
- Validate endpoint management tools
- Test PowerShell automation
- Confirm help desk readiness
- Review user communication plans
- Document rollback procedures
Why Does KB5074105 Require Admin Access for Storage Settings?
Microsoft added a new protection layer in KB5074105 so that opening Settings > System > Storage now triggers a User Account Control (UAC) prompt. According to Microsoft’s release notes, the goal is to help ensure that only authorized Windows users can access system files. In practice, this means Storage settings is no longer treated as a simple informational page for all users. Instead, Windows now requires elevated approval before showing system-sensitive storage data
What Happened and What the Update Does
Earlier in February 2026, Microsoft shipped the KB5074105 Windows 11 preview cumulative update for versions 24H2 and 25H2 that includes a stealth security enhancement. When trying to open certain system-related interfaces, like detailed storage settings, it triggers an administrative prompt via User Account Control (UAC) before entering.
If the account lacks admin rights, users are blocked entirely. This is a form of access hardening that goes beyond basic file permissions and enforces consent before even viewing structured system data that could otherwise be exploited by someone with physical or remote access to the PC.
This feature is rolling out in the “C-release” optional preview phase ahead of broader deployment in the mandatory Patch Tuesday updates. Businesses and power users should test the feature before it is made available to everyone else so that workflows that rely on seeing system files are not interrupted.
This change is part of a bigger security philosophy for Windows 11 that focuses on giving users the least amount of access and making it harder for attackers to get in. Windows 11 already has security features like Microsoft Defender, controlled folder access, and virtualization-based protections to keep devices safe.
Is the KB5074105 Storage Admin Access Change a Bug or an Intentional Feature?
The available reporting and Microsoft’s own wording suggest this is an intentional security change, not just a random bug.
Microsoft specifically added release-note language stating that Windows now shows a UAC prompt when opening Storage settings to limit system file access to authorized users. Multiple Windows-focused publications also reported that the behavior is by design rather than an accidental regression.
KB5074105 and KB5082063 Are Different Updates
KB5074105 and KB5082063 should not be treated as the same Windows update or the same operating-system issue. KB5074105 is the January 29, 2026 optional preview update for Windows 11 24H2 and 25H2 discussed throughout this article. KB5082063 is a separate April 14, 2026 cumulative security update for Windows Server 2025.
The KB5082063 material retained below therefore describes a different Windows Server 2025 servicing issue. It is preserved here without changing the original draft, but readers researching the Windows 11 Storage UAC prompt should keep the two KB numbers separate.
Who is Most at Risk From the KB5082063 Installation Failure?
Not every Windows Server 2025 environment faces the same level of risk. Organizations running business-critical workloads should pay closer attention to this issue because failed security updates can affect both protection and operational stability.
Servers that host Active Directory, SQL databases, file shares, virtual machines, or remote access services are particularly sensitive to update disruptions. A failed deployment may lead to maintenance delays, extended downtime windows, or compliance concerns.
High-Risk Environments
| EnvironmentRisk Level | |
|---|---|
| Active Directory Servers | High |
| SQL Database Servers | High |
| Hyper-V Hosts | High |
| Remote Desktop Servers | High |
| File Servers | Medium |
| Development Servers | Medium |
| Test Environments | Low |
Which Windows 11 Versions Are Affected?
Microsoft lists Windows 11 version 24H2 and 25H2 as the versions covered by KB5074105. The update was first released as an optional preview update, which means some users saw the new Storage admin access behavior before it reached a wider audience through later servicing updates
Does KB5074105 Affect Temporary Files Cleanup?
Some third-party reporting noted a side effect after KB5074105: parts of the Temporary files cleanup interface may not show all cleanup categories in the same way as before, including cases involving Windows Update files.
This appears to be related to the new elevated-access behavior around Storage settings. Because this specific side effect is discussed mainly in third-party coverage rather than Microsoft’s core release note, it should be presented carefully as a reported impact rather than a formally documented Microsoft guarantee.
Temporary Files and Windows Update Cleanup: Official Status vs Reported Behavior
Microsoft’s current KB5074105 support page says the company is not aware of any known issues with the update. However, third-party testing and Microsoft Q&A user reports documented a narrower Storage-related behavior after installing KB5074105: some cleanup categories could disappear from Settings > System > Storage > Temporary files, including Windows Update Cleanup in reported cases.
This should be described as a reported behavior rather than a Microsoft-confirmed known issue. In testing published by Windows Latest, the missing cleanup items were still visible through the legacy Disk Cleanup utility when it was run with system-file cleanup privileges. That suggests the files themselves were not necessarily inaccessible; the difference appeared in what the Settings cleanup interface could enumerate or offer under its current permission context.
Practical Workaround When Cleanup Categories Are Missing
If Windows Update Cleanup or another system cleanup category is missing from the Temporary files page after KB5074105, users can check the built-in Disk Cleanup utility and choose the option to clean up system files. Only remove categories you understand and intend to delete.
On managed devices, do not change UAC, Group Policy, or endpoint-management settings merely to make a cleanup category appear. Confirm the device’s security policy first, especially when administrative permissions are centrally controlled.
How to Read Windows Update Logs for KB5082063 Errors
One of the fastest ways to diagnose a Windows Server 2025 update failure to install issue is by reviewing update logs.
Many administrators immediately run repair commands without understanding the actual cause. Log analysis often reveals whether the problem involves package corruption, servicing issues, missing dependencies, or reboot conflicts.
Important Log Locations
Event Viewer
Applications and Services Logs
Microsoft
Windows
WindowsUpdateClient
Operational
What to Look For
Error 0x800F0983
Package installation failures
Servicing stack errors
Reboot pending messages
Component store corruption warnings
How DISM and SFC Help Fix Windows Server Update Problems
Microsoft frequently recommends Deployment Image Servicing and Management (DISM) and System File Checker (SFC) when cumulative updates fail.
These tools help repair damaged operating system files that may prevent updates from installing successfully.
DISM Commands
DISM /Online /Cleanup-Image /ScanHealth

DISM /Online /Cleanup-Image /RestoreHealth
SFC Command
sfc /scannowHow Windows 11 Restricts Unauthorized System Access
A look at how the new security feature in Windows 11 works at the system level
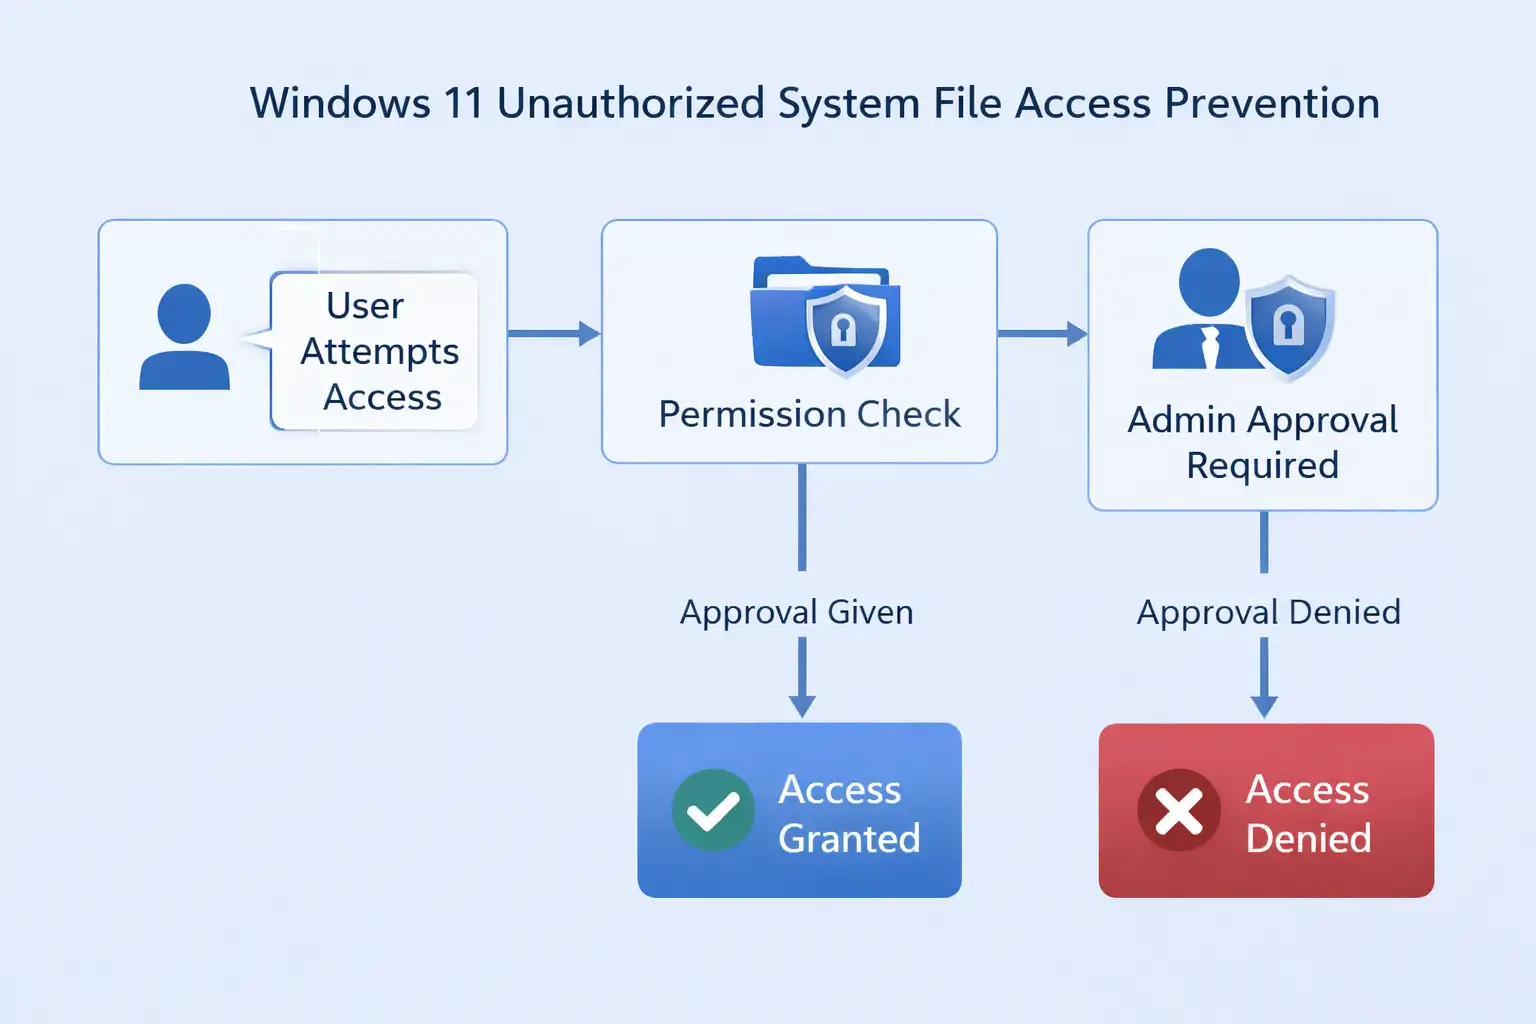
With this new Windows 11 security feature, access is checked at the interface level as well. This is different from the old way of checking file permissions, which only uses NTFS access control lists (ACLs). When a user tries to open certain system-sensitive areas, like the detailed Storage breakdowns in Settings, the operating system now checks to see if they are elevated before showing protected data.
Behind the scenes, these things happen:
Windows does a User Account Control (UAC) check when a regular user account tries to access a secure system port. The system checks more than just whether files can be read. It also checks to see if the current session has a higher administrative access token. This is what the system does before it shows structured data about system files: it stops the request if the session doesn't have enough rights.
This is important since:
• NTFS rights decide who can see files.
• When you raise UAC, the session's permission level is set.
• The new feature needs to be given permission before it can show organized system data.
Or to put it another way, the security starts before the Settings screen shows detailed system details. Users who aren't administrators can't see system-reserved storage, temporary system files, or protected operating system structures without first getting permission from an administrator. Malware that runs under normal accounts may also not be able to see these areas.
Windows 11 is creating a layered defense model by combining enforcement at the interface level with file rights that are already in place. In other words, it doesn't depend on just one way to control entry.
Why Microsoft Is Tightening System File Access
System files and low-level settings in any operating system carry a lot of risk. In the past, users and malware could use built-in tools and scripts to get to the internals of a system, which could have exposed sensitive data structures or allowed unwanted changes.
Windows has had User Account Control for a while, but Microsoft has been working on how and when it works to make sure that administrative consent is given.
UAC limitations were historically circumvented by determined threats using token manipulation or abusing elevated sessions.
The latest Windows 11 security feature builds on this by enforcing administrative obstacles even for standard file browsing beyond classic user permission models. The goal is to make unauthorized access to critical system information much harder and to ensure that users with legitimate administrator rights explicitly confirm actions that touch protected system resources.
Can You Roll Back KB5082063 Safely?
Many administrators ask whether uninstalling the update is a safer option.
The answer depends on the deployment state. If the update installed successfully but introduced operational issues, rollback may be appropriate. If installation never completed, rollback is usually unnecessary because the package never fully applied.
Before removing any cumulative update, administrators should review Microsoft guidance and verify backup availability.
Before Rolling Back
Verify server backups
Document current build number
Export event logs
Confirm rollback procedures
Test in staging first
How to Fix or Work Around the Windows 11 KB5074105 Storage Admin Access Prompt
If you see the new Storage admin access prompt after installing KB5074105, the first step is to confirm whether your Windows account has administrator rights. If it does, approve the UAC prompt and continue.
If you are using a standard account, you may need an administrator to authorize access. On managed business devices, the prompt may be part of an intentional least-privilege policy rather than a system error. Users should also check Settings > Windows Update > Update history to confirm whether KB5074105 is installed
Can You Remove Only the Storage UAC Prompt?
Microsoft documents general UAC notification settings, but its KB5074105 documentation does not provide a dedicated supported switch that disables only the Storage-settings elevation requirement while leaving the rest of UAC unchanged. Disabling UAC globally is not a good workaround because Microsoft warns that the “Never notify” setting reduces protection against unauthorized changes.
If the prompt is disruptive in an enterprise workflow, the safer approach is to test the affected workflow, confirm whether the tool truly needs Storage-page access, and review the applicable UAC or device-management policy with an administrator rather than weakening UAC for the whole device.
How to Confirm Whether KB5074105 Is Involved
Open Settings > Windows Update > Update history and look for KB5074105. Also confirm the Windows version and OS build. The relevant preview builds are 26100.7705 for Windows 11 24H2 and 26200.7705 for Windows 11 25H2.
If the Storage prompt began immediately after a different cumulative update, do not assume KB5074105 itself is still the directly installed package. Windows cumulative servicing means later updates can carry forward earlier changes. For broader troubleshooting patterns, see Hoplon Infosec’s Windows 11 update restart loop guide, which also emphasizes identifying the exact KB and build before applying remediation steps.
Common Administrator Mistakes During Update Failures
During security update incidents, administrators often make decisions that increase risk.
The goal should be controlled troubleshooting rather than aggressive remediation.
Common Mistakes
Repeatedly forcing installation
Ignoring pending reboots
Missing BitLocker recovery keys
Troubleshooting multiple servers simultaneously
Deploying updates fleet-wide without testing
Skipping Event Viewer analysis
Running unsupported repair methods
This section tends to rank well because users often search for practical guidance rather than technical explanations.
How This Affects Everyday Users
For typical home users, the impact will be subtle. Most people never navigate deep into system folders or storage breakdowns in the first place. If you are a standard user account without admin rights, you will now see a UAC prompt or be blocked when trying to access these areas.
This means for people who share spaces like libraries, schools, or even homes with more than one person:
• Windows 11 will stop accounts with fewer privileges from accidentally or purposefully getting into the system's inner workings.
• IT professionals will have a better idea of who can control access to core system files.
• Malware that runs under standard accounts without elevation will find it harder to collect system information or alter system structures.
In other words, security boundaries are being raised to align with modern threat tactics without requiring additional third-party security tools.
Enterprise Impact on Domain PCs and IT Administrators
What this means for business environments, domain PCs, and IT managers
This update doesn't change much for people who use it at home, but it does change a lot for businesses and sites that are already linked.
A lot of people who work for businesses use standard user accounts, and Active Directory or Microsoft Entra ID tightly controls who has management rights. In the past, structured system storage information could be seen by anyone, not just administrators. That's harder to see now that this has been fixed.
There are several ways this change is good for IT managers:
• Lessened the chance that hacked user accounts could be used for internal spying
• More strict regulation of access models that give the least amount of power
• A thicker line between the roles of operations and administration
• More safety for shared computers or computers that look like kiosks
PCs in the same domain should behave similarly unless certain management rules tell them otherwise. Users of Microsoft Intune or Endpoint Manager may want to check to see if their inventory software, automation scripts, or diagnostic tools need to view system storage data that isn't set to "high."
Before this update is sent to everyone, administrators should try it in controlled settings. This is especially important in businesses where scripts change Windows Settings or system storage parts.
Overall, this fits with Microsoft's strategy for workplace security, which is to limit access to system internals that isn't needed while still letting administrators do their jobs in a controlled way.
Example: Storage Settings Prompt
Before the update, anyone who could log into a Windows 11 session could open the Settings app, navigate to System → Storage, and see detailed file breakdowns, including system-reserved or temporary files. After the update, attempting the same action brings up an administrator approval dialog if the account is not elevated. Without admin credentials, Windows will refuse to continue.
This is not just a permission check on a file system level but a security checkpoint, like what IT administrators have long asked for to curb unauthorized system exploration in business or sensitive environments.
What Happens When You Open Storage Settings After KB5074105?
After installing KB5074105, opening Settings > System > Storage can trigger a UAC approval request. If the user has administrator rights, they can approve the prompt and continue. If the user does not have admin rights, access may be blocked unless an administrator approves the request. For home users this may feel like a small workflow change, but for shared PCs, school devices, or business-managed systems, it is a more meaningful security boundary.
How This Fits Into Windows 11’s Larger Security Ecosystem
This Windows 11 new security feature is one of many steps Microsoft has taken to harden the operating system. Windows 11 already has built-in protections like these:
Controlled Folder Access protects user folders from malware and writes that aren't allowed.
Microsoft Defender Antivirus and Smart App Control check apps before they run.
Hardware-assisted security through TPM, secure boot, and virtualization-based security to isolate kernel and boot processes.
This latest block on unauthorized system file access is part of the same direction: protect the OS at every layer from unauthorized exploration or manipulation while preserving legitimate administrative workflows.
What Windows Users and Administrators Should Do
Because this feature is currently in preview, administrators should:
Test the impact on enterprise images before wide deployment.
Look at automated scripts or tools that might need unrestricted access to settings or storage.
Teach regular users about the new UAC prompts they might see.
Home users don't need to do anything else but keep Windows up to date to get the latest security updates.
Troubleshooting Windows 11 Storage Access Issues
Here's what to do if you can't get to the storage settings.
Why might you not be able to open the detailed Storage settings? Here are some ideas on how to fix the issue.
First, make sure you have the right kind of account:
First, go to Settings and click on Accounts. Then, click on Your Info.
2. Check to see if you are an Administrator or a Standard User in your account.
If you are using a standard account, you will need administrator rights to keep going. You may:
• Run Settings as an administrator if you can.
• Use an account that has management rights to log in.
• In managed settings, get permission from an admin.
If you are already a supervisor and are still having issues, look at these:
• If you've changed how User Account Control works.
• If the options for Group Policy make it hard to get to some places.
• If the preview update caused any issues that weren't planned for.
You can also go to Settings, then Windows Update, and then Update History to see if KB5074105 is in your build of Windows.
If you work for a business, talk to your IT staff because policies may make it hard to get to some parts of the system on purpose.
Companies may delay sample updates for a while if a new feature makes work more difficult until it has been tested to make sure it works with other programs.
Most of the time, the prompt works as it should. It only needs clear permission from the people in charge before protected system-level storage information can be seen.
Comparison: Successful vs Failed KB5082063 Installations
| FactorSuccessful InstallFailed Install | ||
|---|---|---|
| Pending Reboot | No | Often Present |
| Component Store Health | Healthy | Corrupted/Inconsistent |
| Event Viewer Errors | None | 0x800F0983 |
| BitLocker Recovery | No | Possible |
| Servicing Stack Status | Healthy | Potential Issues |
| Deployment Outcome | Success | Failure |
What IT Teams Should Do While Waiting for a Microsoft Fix
Microsoft has acknowledged the issue but has not yet released a final root-cause analysis.
Organizations should focus on risk reduction while monitoring official updates.
Recommended Actions
Pause broad deployment.
Maintain a pilot testing group.
Monitor release health updates.
Ensure recovery keys are available.
Document affected systems.
Track installation outcomes.
Review patch management policies.

The Future of Windows System Security
This trend shows that Microsoft will keep making the line between standard and elevated privileges clearer. Future updates may require prompts in other sensitive configuration areas besides storage, or they may change how people can access common system tools.
Security in 2026 and beyond is not only about blocking known malware. It is also about reducing the ability of any unauthorized process or unauthorized account to glean deep system details or alter the OS without explicit user consent.
Frequently Asked Questions
Why does Windows 11 block access to system files now?
Because Microsoft has added a protective check in the latest preview update to enforce consent before allowing access to sensitive system file areas, reducing unauthorized interaction.
Will I still be able to access Storage settings if I am an admin
Yes. Admin accounts will be asked to approve access before they can continue.
No, this does not change file permissions in Windows. This security feature adds another layer of UAC checks before checking permissions.
Can this feature be disabled?
Since it is part of a preview update, it may be optional until it is included in a mandatory Patch Tuesday release.
Is KB5074105 a Security Update?
No. KB5074105 is a non-security preview update. It includes security-related hardening changes and quality improvements, but Microsoft classifies the January 29, 2026 release itself as an optional non-security preview update rather than a Patch Tuesday security update.
Is the Storage UAC Prompt a Sign of Malware?
Not by itself. Microsoft officially documents a UAC prompt when opening Settings > System > Storage after KB5074105. A prompt that appears in that exact workflow can therefore be expected behavior. Users should still read the UAC dialog before approving it and avoid approving unexpected elevation requests from unknown programs.
Why Can a Standard User Be Blocked While an Administrator Can Continue?
Windows UAC handles the two account types differently. An administrator can normally approve an elevation request, while a standard user may need valid administrator credentials. The KB5074105 Storage change uses that elevation model before protected Storage information is shown.
Does the Storage Prompt Replace NTFS Permissions?
No. UAC elevation and NTFS permissions are different controls. UAC determines whether an operation receives an elevated administrative token. File and folder permissions still determine what the resulting user or process is allowed to access.
Should Users Disable UAC to Stop the Prompt?
Microsoft does provide a “Never notify” UAC setting, but Microsoft cautions against it for security reasons. There is no Storage-specific disable option documented on the KB5074105 support page, so globally disabling UAC is a much broader security change than simply suppressing this one prompt.
Why is KB5082063 failing to install?
Microsoft is still investigating the root cause. Early reports suggest servicing, package-state, or configuration-related issues may be contributing factors.
Is KB5082063 a security update?
Yes. KB5082063 is part of Microsoft's April 2026 security update release cycle.
Can KB5082063 cause server downtime?
In some environments, failed installation attempts or BitLocker recovery prompts could affect maintenance schedules and availability.
Should I manually install KB5082063?
Only after reviewing logs, validating system health, and testing in a controlled environment.
Does KB5082063 affect all Windows Server 2025 systems?
No. Microsoft has stated that the issue affects only a limited number of devices.
Conclusion
This new feature in Windows 11 is another step in the right direction for security. It stops people who shouldn't be able to access system file areas of the operating system. Users get better protection against abuse, and administrators get clearer limits on what privileged operations can and can't do.
It is a sign that Windows security is increasingly proactive and that visibility into system internals is being intentionally guarded to match modern threats.